Industry Insights
5 Best Secureframe Competitors and Alternatives in 2026

If you're comparing Secureframe against other compliance automation tools before a renewal or a first purchase, you're not alone. Most buyers evaluating Secureframe alternatives land here for the same reason: the platform's audit-first design starts to feel too narrow once day-to-day compliance work kicks in.
This guide covers the best Secureframe competitors in 2026: Valiido, Vanta, Drata, Strac Comply, and AuditBoard. You'll get a full review of each tool, a comparison table, and a breakdown of how to choose the right compliance automation platform.
Key Takeaways
- Valiido: Best for ISO® 27001 and TISAX® certification without a consultant, built around focused ISO® 27001 and TISAX® depth rather than broad enterprise GRC.
- Vanta: Best for SaaS startups chasing a fast first SOC 2; keep in mind pricing scales quickly with company size.
- Drata: Best for teams managing multiple frameworks with deeper automation; the tradeoff is renewal price jumps.
- Strac Comply: Best for security teams that need native DLP and DSPM alongside audit evidence; just know the integration library is smaller than the market leaders'.
- AuditBoard (now Optro): Best for large enterprises running SOX and internal audit programs; the catch is pricing that's out of reach for small organizations.
What makes Valiido different is simple: it strips out the enterprise complexity that mid-market teams don't need and focuses entirely on ISO® 27001 and TISAX® certification.
Instead of a bloated GRC suite, you get a guided, software-led path that replaces the consultant most competitors still assume you'll need.
AuditMagic checks your security controls automatically, flags failing tests before your auditor does, and keeps your compliance status current.
That's the profile most buyers have in mind when they look for a Secureframe alternative that skips a six-figure contract.
If you want the detailed, feature-by-feature breakdown, the Valiido vs. Secureframe comparison walks through exactly where the two platforms diverge.
See your own audit preparation process take shape: start for free today.
Why Teams Look for Secureframe Competitors
Secureframe built its platform around audit preparation, and buyers start looking elsewhere once a few specific gaps show up.
- Its audit-first orientation can slow down continuous, day-to-day compliance work once you're certified.
- Native DLP and DSPM controls are limited, pushing some buyers toward a combined stack.
- Enterprise teams increasingly need vendor risk management and risk assessment depth beyond certification prep.
- Adding frameworks later often means duplicate work instead of clean cross-framework mapping.
- Pricing isn't public, and renewal jumps catch some teams off guard.
That gap between passing an audit and staying audit-ready is why continuous monitoring matters more than a one-time check. Evidence needs to stay current between audits, not just before them.
Skipping this step often means scrambling again next year, one of 7 reasons your ISMS isn't audit-ready.
Secureframe Competitors Compared: Ratings, Pricing & Fit
If you're preparing for your first audit, you can use this table to weigh rating, pricing, and best fit before you narrow your shortlist.
| Tool | G2 Rating | Best For | Top Feature | Starting Price |
|---|---|---|---|---|
| Valiido | 4.9/5 | Small organizations pursuing ISO® 27001 or TISAX® without a consultant | AuditMagic automated gap checks | €149/month |
| Vanta | 4.6/5 | SaaS startups pursuing a first SOC 2 | Automated evidence collection across 375+ integrations | Custom quote |
| Drata | 4.7/5 | Teams managing multiple compliance frameworks at once | Continuous control monitoring | Custom quote |
| Strac Comply | 4.3/5 | Security teams that want DLP and DSPM bundled with compliance | Real-time sensitive data discovery and redaction | Custom quote |
| AuditBoard | Not available | Large enterprises running SOX, ERM, and internal audit | Centralized enterprise GRC workflows | Custom quote |
Want a wider view first? Compare the 10 best ISMS software tools.
The Best Secureframe Alternatives in 2026
Reading feature lists side by side rarely tells the full story. Pay attention to what each tool leaves out, not just what it includes.
Valiido
Valiido is an all-in-one ISMS compliance automation platform built for companies pursuing ISO® 27001 and TISAX® certification. It replaces consultant-led projects with a self-serve platform teams can run on their own, changing both the cost and timeline of certification.
Best for
Small and mid-sized companies that want a structured audit preparation process without hiring outside help.
Key features
- Valiido Guide: A chapter-by-chapter walkthrough that shows exactly what to complete next for ISO® 27001 and TISAX®, cutting the manual effort of starting from scratch.
- 1-Click Templates: Over 200 ready-to-use documents and policies in English and German, so teams can collect evidence and build their ISMS without writing every policy from zero.
- AuditMagic: Automatically reviews every record against ISO® 27001 and TISAX® best practices, flags failing tests, and generates weekly reports so evidence current status stays visible.
- Built-in modules: Risks, audits, vendors, assets, incidents, and KPIs live under one roof instead of scattered spreadsheets.
See Valiido's full feature set for the complete module list.
Pricing
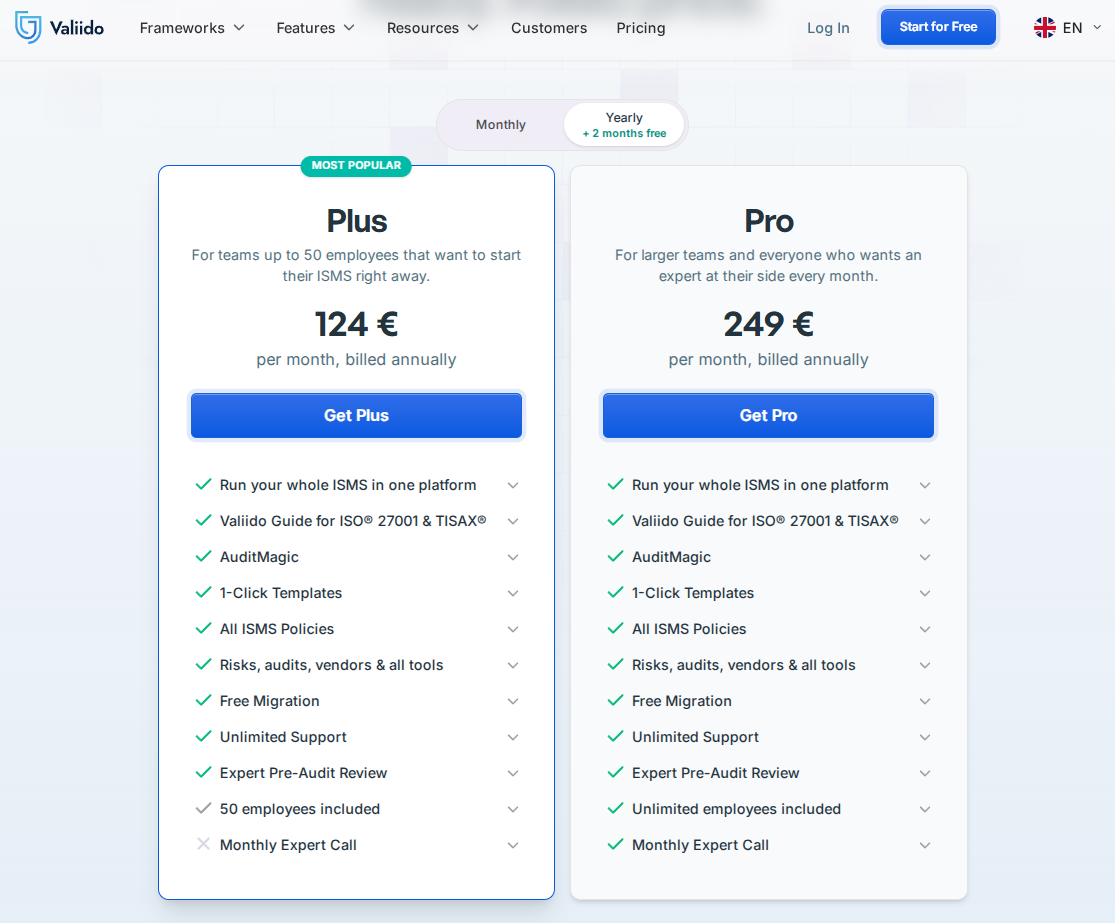
Valiido runs on a transparent pricing model that starts at €149 per month or €124 per month billed annually, with 50 employees included as a flat rate and no setup fee.
There's no per-document charge and no consultant add-on required. For the full picture of what that price covers, read the Valiido pricing breakdown.
Start for free and see your own ISMS take shape in minutes.
Vanta
Source: Vanta website screenshot. Reviewed August 26, 2026.
Vanta has become one of the category-defining compliance automation platforms for cloud-native companies moving quickly toward certification. It's backed by a large integration library and years of enterprise adoption. Vanta's approach centers on plugging into your existing stack rather than asking teams to change how they work.
Best for
Cloud-native SaaS businesses that need multi-framework support and broad framework coverage across SOC 2, ISO® 27001, HIPAA and PCI DSS.
Key features
- Automated evidence collection: Connects to 375+ tools to pull audit evidence continuously instead of chasing screenshots.
- Trust center: A public-facing page that shares live compliance status with prospects during sales cycles.
- Cross framework mapping: Maps shared controls once and applies them across additional frameworks, cutting duplicate work.
- Vendor risk management: Tracks third-party risk assessment tasks alongside internal controls.
Pricing
Vanta doesn't publish list pricing. According to SOC2Auditors, reported contracts start around $10,000 a year for a single framework and scale with company size, seats, and the number of frameworks in scope.
See how this stacks up in the full Valiido vs Vanta compared breakdown.
Drata
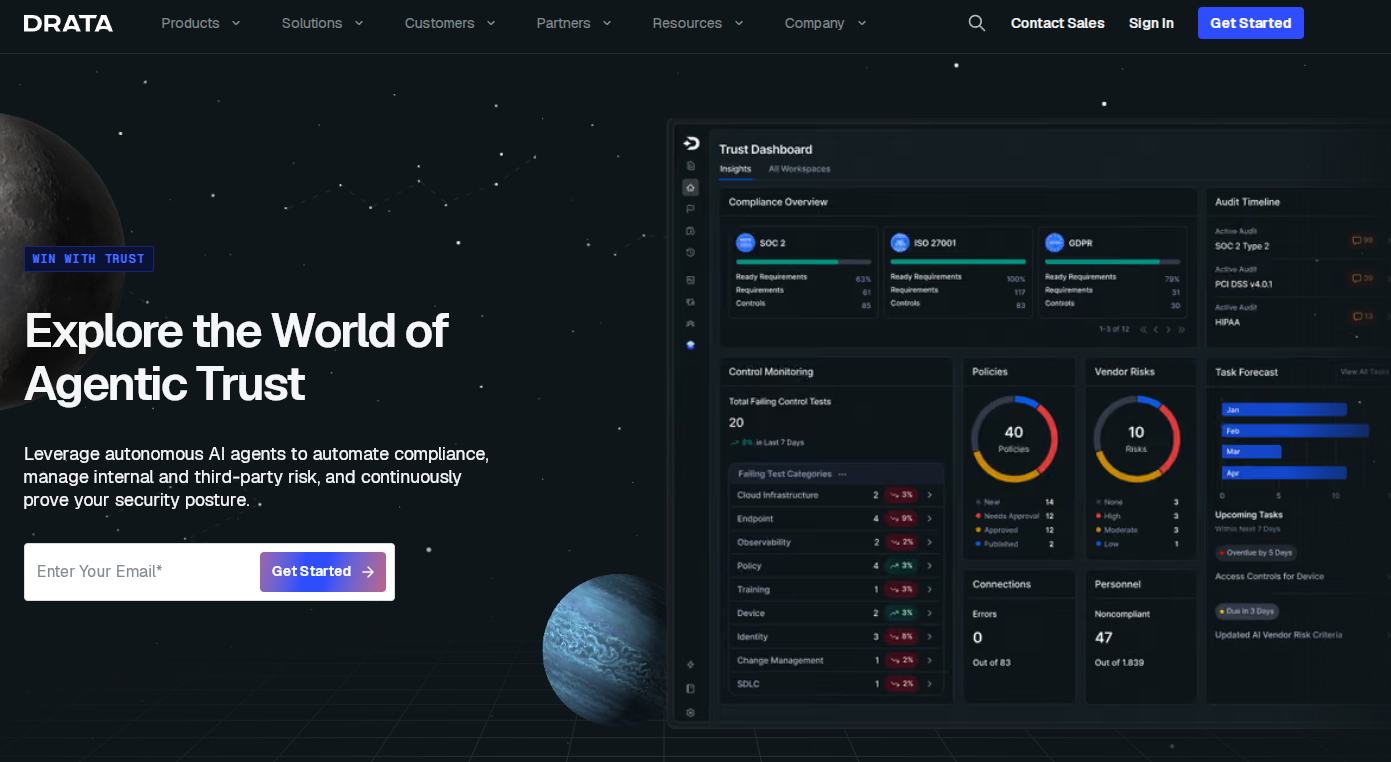
Source: Drata website screenshot. Reviewed August 26, 2026.
Drata built its reputation on continuous compliance rather than treating certification as a one-time push. Founded in 2020, it has scaled quickly and become one of the two platforms most startups shortlist alongside Vanta. Its dashboard gives teams a live read on their security posture between audits, not just before them.
Best for
Growth-stage teams that need deeper automation across SOC 2, ISO® 27001, HIPAA, and additional frameworks as they scale.
Key features
- Continuous control monitoring: Hourly checks flag failing tests in near real time instead of a manual review cycle.
- Cross-framework mapping: One shared control satisfies several frameworks at once, reducing duplicate work as programs grow.
- Risk management: Built-in risk assessment workflows help teams manage risk alongside audit evidence.
- Auditor collaboration workspace: A shared portal that keeps auditors, security teams, and engineers on the same evidence set.
Pricing
Drata doesn't publish list pricing either. According to SecureLeap, reported contracts start near $7,500 a year for a single framework, with mid-market teams landing between $20,000 and $40,000 annually.
Compare the details in Valiido vs Drata.
Strac Comply
Source: Strac Comply website screenshot. Reviewed August 26, 2026.
Strac Comply takes a different angle than most compliance automation platforms here. It folds data security directly into the same platform that handles audit evidence, instead of treating it as a separate purchase.
That combination appeals to teams that don't want to stitch together two separate vendors. It holds a 4.9 out of 5 rating on G2, the software review platform buyers use to compare verified feedback.
Best for
Security teams that need real-time data protection built into their compliance automation, not layered on top.
Key features
- Sensitive data discovery: Scans Slack, email, cloud storage, and SaaS apps for PII, PCI, and PHI, then flags it automatically.
- DSPM and DLP in one policy engine: Covers SaaS, cloud, endpoint, and AI agent surfaces under one set of rules.
- Framework coverage: Maps controls to SOC 2, ISO® 27001, HIPAA, and GDPR from the same evidence layer.
- Automated remediation: Redacts, masks, blocks, or revokes access to sensitive data without manual work.
Pricing
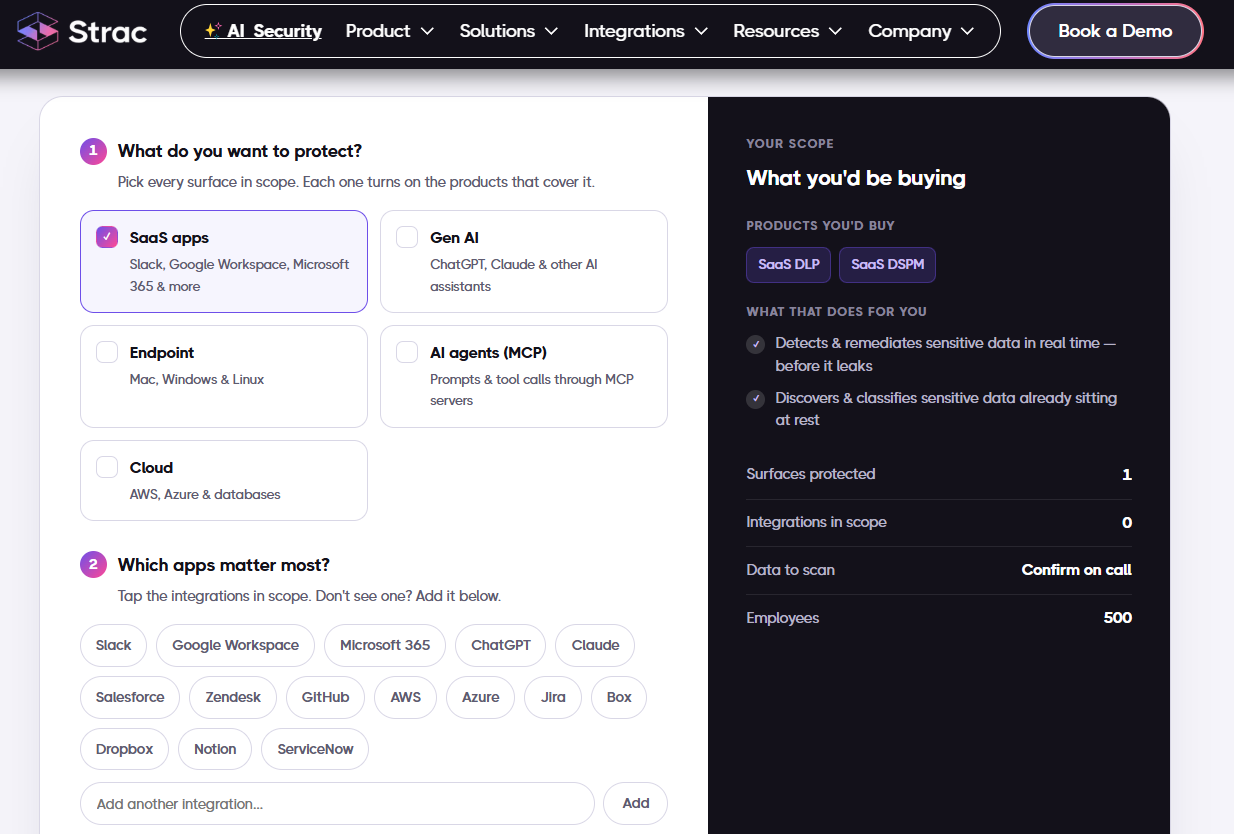
Source: Strac pricing page screenshot. Reviewed August 26, 2026.
Pricing is custom and modular. You can buy a single product, like SaaS DLP or Gen AI DLP, or the full platform, and the quote is based on the number of employees actually in scope for what you buy, not your entire company directory.
Real-time protection isn't priced on data volume, but historical discovery scans do factor in how much existing data needs to be reviewed.
AuditBoard (now Optro)
Source: Optro website screenshot. Reviewed August 26, 2026.
AuditBoard rebranded as Optro in March 2026, following Hg Capital's 2024 acquisition, but it's still the same enterprise GRC platform for internal audit, SOX compliance, and risk oversight at scale.
It now runs on a unified data core, so controls, risks, policies, and evidence tested in one module carry over automatically to the others instead of living in separate silos.
Best for
Large enterprises with dedicated audit and risk teams that need enterprise GRC depth beyond certification prep.
Key features
- SOXHUB: Optro's original module, still built for SOX 404 controls testing and internal controls over financial reporting.
- RiskOversight: The platform's enterprise risk management module, centralizing the risk register and remediation tracking across business units.
- TPRM: Third-party risk management workflows built for procurement and audit teams at enterprise scale.
- Unified data core: Connects every module for real-time visibility, giving audit and risk leaders actionable insights into compliance programs.
Pricing
Pricing isn't published. According to ComplianceRated, reported contracts typically run from $30,000 to $80,000 or more a year depending on modules and company size, with Vendr-tracked deals for specific modules like SOXHUB Professional running $42,000 to $125,000 depending on term length.
How to Choose the Right Secureframe Alternative
Choosing the right compliance automation platform comes down to three factors. Consider how continuous your monitoring needs to be, whether you need native data security, and how deep your risk management must go.
Audit-first versus continuous compliance depth
Audit-first tools get you certified fast but can fall short once the audit ends. Continuous monitoring tools cost more upfront but keep your compliance status current year-round, which matters if you're managing many frameworks or facing frequent audits.
Native DLP, DSPM, and AI governance checks
If your data lives across dozens of SaaS apps and AI tools, check whether native integrations for data discovery are built in or bolted on.
A platform with basic automation for evidence collection but no real data security layer leaves exposure unchecked, no matter how many failing tests it catches.
Weigh each finalist's automation capabilities against your actual data footprint.
Enterprise GRC and risk management depth
Large enterprises need vendor risk management, remediation tracking, and cross-department reporting that a lean compliance automation tool wasn't built for. Smaller organizations rarely need that depth, and often find it adds cost and limited customization options instead of speed.
| Decision Factor | What to Check | Why It Matters |
|---|---|---|
| Audit-first vs continuous | Does the platform monitor controls daily or only before an audit? | Determines whether you stay audit ready year-round |
| Native DLP/DSPM presence | Is data discovery built in, or does it need a second vendor? | Affects total cost and how fast exposure gets caught |
| Enterprise GRC depth | Does it support SOX, ERM, and multi-department reporting? | Matters for large enterprises, overkill for small organizations |
| Pricing and renewal terms | Is pricing public, and what happens at renewal? | Reported renewal jumps are common across quote-based vendors |
Want a fuller framework? Read how to choose ISMS software before you sign anything.
Secureframe vs Alternatives: Recommendation by Use Case
- Choose Valiido if you're a small or mid-sized team pursuing ISO® 27001 or TISAX® and want to skip the consultant.
- Choose Vanta if you're a cloud-native SaaS startup that needs a fast first SOC 2 and broad integrations.
- Choose Drata if you're managing multiple frameworks and need deeper automation as your program grows.
- Choose Strac Comply or AuditBoard if you need native data security bundled in, or enterprise GRC depth for SOX.
For teams with ISO® 27001 or TISAX® compliance needs, Valiido remains the strongest all-around pick because it delivers audit readiness without enterprise pricing or a consultant on retainer.
A Closer Look at Valiido
Valiido sits between spreadsheets and enterprise GRC platforms. It costs less and starts faster than a four-figure-a-month tool, while offering more structure than an Excel-and-Word setup where you write every policy from scratch.
Founder Christopher Eller built the platform after years of working across IT, security, and compliance in the automotive industry. He holds qualifications as an ISO® 27001 auditor, data protection officer, and risk manager.
Every plan includes live chat plus a pre-audit review before you meet an actual auditor.
Two plans cover most teams. Plus runs €149 per month, or €124 per month billed annually, for up to 50 employees. It includes every module, plus a free migration if you're moving an existing ISMS out of Word or Excel.
Pro runs €299 per month, or €249 per month billed annually, drops the employee cap, and adds a monthly call with an expert.
The platform is EU-hosted, which matters if data residency is part of your framework requirements.
It also holds a 4.9 out of 5 rating from 29 reviews. That combination makes it a solid pick for a company that wants a guided path rather than a blank workspace.
Start for free to see the platform for yourself.
Switching from Secureframe: Migration Checklist
Ready to move off Secureframe? Many teams rush this step, but these four phases help Secureframe users keep the transition clean and avoid gaps in compliance status.
- Export all evidence, policies, and audit history from Secureframe before canceling.
- Map existing controls to the new platform's framework structure, including shared controls across SOC 2 and ISO® 27001.
- Run both platforms in parallel for one monitoring cycle to confirm evidence collection works correctly.
- Decommission Secureframe only after your new platform passes a full internal review.
Rebuilding your ISMS from scratch as part of the switch? Building an ISMS without a consultant walks you through it step by step.
Conclusion About Secureframe Competitors
Secureframe has real competition, and each alternative here solves a different piece of the puzzle. Vanta and Drata push deeper into continuous monitoring, Strac Comply folds in native data security, and AuditBoard handles enterprise-scale GRC.
Valiido remains the strongest overall pick for teams focused on ISO® 27001 and TISAX®, since it delivers a full audit preparation process at a fraction of the cost.
Try Valiido free and get your ISMS moving today.
Frequently Asked Questions
What is the best compliance management software?
The best compliance management software depends on your framework and company size. Valiido fits small teams pursuing ISO® 27001 or TISAX® without a consultant; Vanta and Drata suit SaaS companies scaling across multiple frameworks, and AuditBoard fits large enterprises running SOX programs.
Who are Secureframe's main competitors?
Secureframe's main competitors include Valiido, Vanta, Drata, Strac Comply, and AuditBoard. Valiido focuses on ISO® 27001 and TISAX® for smaller teams. Vanta and Drata compete on continuous monitoring, Strac Comply adds native data security, and AuditBoard serves enterprise GRC and SOX programs.
What is Secureframe?
Secureframe is a security compliance automation platform that helps companies prepare for SOC 2, ISO® 27001, HIPAA, and other certifications. It automates evidence collection, maps controls across frameworks, and supports audit preparation for growing SaaS businesses. Buyers typically compare it against Vanta, Drata, and other Secureframe alternatives first.
How much do Secureframe alternatives cost?
Pricing varies widely. Valiido publishes transparent pricing from €149 per month. Vanta, Drata, Strac Comply, and AuditBoard use custom, quote-based pricing that scales with company size and frameworks, ranging from $7,500 to well over $75,000 a year.
Do I need a consultant to switch compliance automation platforms?
No. Most compliance automation platforms, including Valiido, guide teams through setup without outside consultants. A consultant can still help with complex, multi-framework enterprise programs, but small teams usually manage the switch internally using built-in guidance.
How we evaluated & sources
This comparison was reviewed on August 26, 2026. It uses publicly available official product, framework and pricing pages from Secureframe, Valiido, Vanta, Drata, Strac Comply and Optro, plus G2 ratings and publicly reported contract ranges from third-party pricing trackers where a vendor does not publish list prices. We selected five alternatives that overlap with Secureframe while serving different needs: focused ISMS implementation, broad multi-framework automation, integrated data security and enterprise GRC. We compared product scope, framework focus, automation approach, pricing and intended team fit. The order is not a numerical ranking. Details about Valiido also reflect direct product knowledge. Third-party screenshots are identified by source and review date.
- Secureframe - Platform
- Secureframe - Frameworks
- Secureframe - Pricing
- Valiido - Features
- Valiido - Pricing
- Vanta - Automated Compliance
- Vanta - Pricing
- Drata - Multi-Framework Support
- Drata - Plans and Pricing
- Strac Comply - Compliance Platform
- Strac - Data Security Pricing
- Optro - AuditBoard is Now Optro
- Optro - Third-Party Risk Management