Industry Insights
5 Best ISO® 27001 Compliance Automation Tools for 2026

ISO® 27001 compliance automation tools replace manual Annex A checks, scattered risk assessments, and last-minute evidence chasing. Instead, a system runs continuously in the background and does the work for you.
If you are still emailing department leads for screenshots before every audit, you already know the cost in hours and stress.
This guide is for founders, IT leads, and compliance officers who want to manage compliance programs without hiring an expensive outside consultant.
We will rank five platforms that treat ISO® 27001 as a core framework, not an add-on. We will also compare how automated the audit process really is, how deep the standard mapping goes, and how much guidance you get without a dedicated compliance hire.
The tools on this list are built to match your compliance requirements, not the other way around.
What Are ISO® 27001 Compliance Automation Tools?
ISO® 27001 compliance automation software automates evidence collection, control monitoring, and audit prep against the standard. It replaces manual Annex A tracking with a compliance management platform built around an information security management system, the formal structure ISO® 27001 actually certifies.
The platform connects to your cloud services and identity provider, pulls data from your existing systems, and cuts down on repetitive tasks. It automates routine compliance tasks and keeps a running record of your compliance status.
Three things decide which one fits: how much is actually automated versus just tracked, how deep the mapping to the standard goes, and how much guidance you get if you are new to certification.
Signs your ISMS still runs on manual compliance work
A few signals suggest your ISMS still runs on manual effort rather than a real platform:
- Control evidence gets chased down by email before every audit, instead of a system built to collect evidence automatically and store it in one place.
- Annex A coverage stays unclear, so evidence requests turn into scavenger hunts.
- Risk and vendor records live in separate spreadsheets that never talk to each other.
- Recertification feels like starting over instead of a light annual refresh.
Any one of these alone is manageable. Together, they mean people are running your ISMS instead of a system.
See what Valiido includes if any of this sounds familiar. It is built to remove these bottlenecks for smaller teams.
How We Evaluated and Ranked These Tools
To keep this list honest, we built it around a fixed set of criteria and a defined selection process. That way, you are not just getting our opinion on familiar logos.
Each platform was assessed against the same six factors:
- How deep the continuous control monitoring actually goes
- Whether evidence automation and audit management cover more than just document storage
- Whether data security controls are built in, not bolted on from a separate tool
- Support for internal audits, with clear control ownership across the compliance team
- Whether operating effectiveness is tracked over time, not just checked once for certification audit readiness
- How transparent the pricing is, and how responsive vendor management actually is
We weighted automated compliance and audit readiness heavily on purpose. A cheap tool that still makes you chase evidence manually is not actually saving you any time.
How We Picked the Products on This List
We started with established ISO® 27001 automation vendors and a few newer specialist players. Then we removed tools where ISO® 27001 is only a minor add-on to a broader GRC suite.
We then ranked what is left by compliance team size fit and automation depth. The result is a shortlist built for real fit, not name recognition.
For more on our approach, see our comparison of ISMS software platforms.
Quick comparison of the best ISO® 27001 compliance automation tools
Here is the shortlist side by side before we go deeper on each one.
| Tool | G2 Reviews | Best For | Key Differentiator | Starting Price |
|---|---|---|---|---|
| Valiido | 4.9/5 | SMBs pursuing ISO® 27001/TISAX® without a consultant | Guided, chapter-by-chapter path with weekly automated audit reports | €149/month |
| Scytale | 4.8/5 | Teams that want AI-driven evidence automation with expert support | Scy, an AI GRC agent, plus a dedicated audit partner | Custom quote |
| Strac Comply | 4.9/5 | Teams that need native DLP alongside ISMS features | Built-in DLP/DSPM so the security control is itself the evidence | Custom quote |
| LogicGate | 4.6/5 | Enterprises with complex, multi-framework GRC needs | No-code Risk Cloud platform with financial risk quantification | Custom quote |
| Optro | 4.6/5 | Mid-market and enterprise teams managing many frameworks | Connected risk core linking ISO® 27001 to 40+ other frameworks | Custom quote |
Valiido leads on transparent, flat pricing and a fully guided path. The other compliance platforms here use quote-based pricing and a configuration-heavy setup.
See Valiido's pricing plans for the full breakdown.
The Best ISO® 27001 Compliance Automation Tools, Reviewed
Here you will find a closer look at each platform, covering what it does, who it fits best, and what it costs, so you can see how the options actually stack up against each other.
Valiido
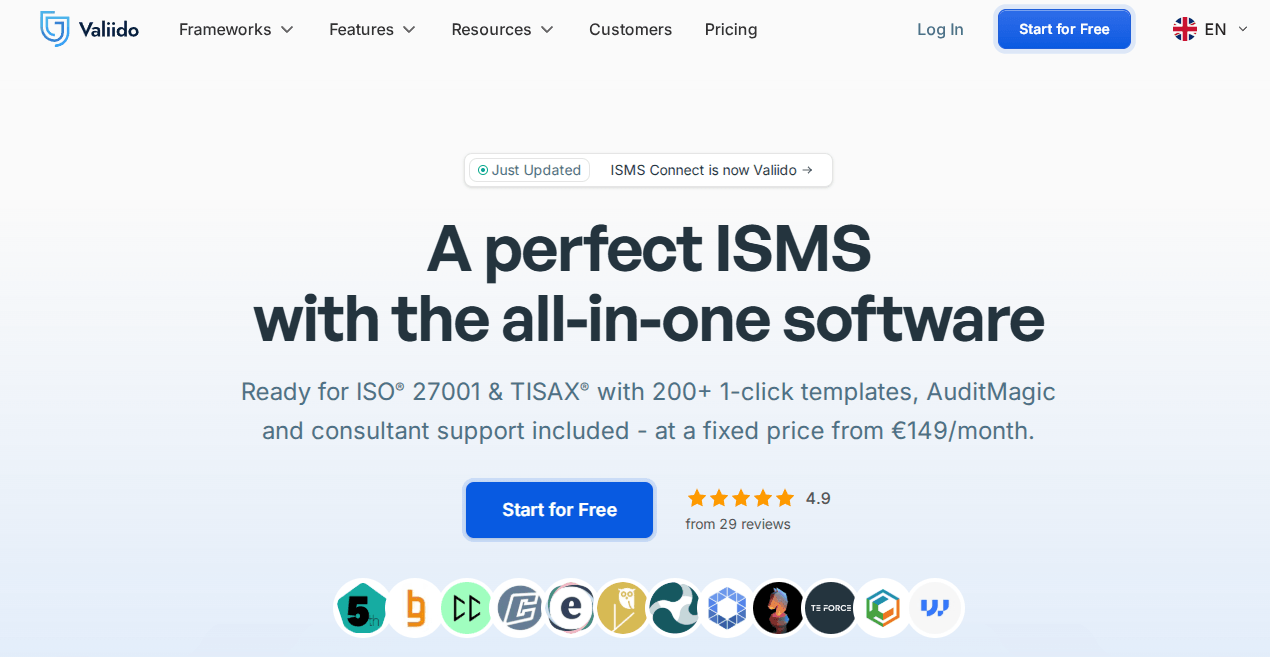
Valiido combines guidance, documentation, and automated gap-checking into a single ISMS workspace for ISO® 27001 and TISAX® certification.
Its built-in template library covers ISMS policies, risks, vendors, and audits, so teams do not have to build documentation from scratch or piece together separate consultant engagements to get there.
Formerly known as ISMS Connect, Valiido runs on a flat-priced, self-service model. That sets it apart from the quote-based, configuration-heavy setup most competing platforms use.
Best for
Companies under 150 employees running their ISO® 27001 or TISAX® program without a consultant.
Key features
- Valiido guide: Walks teams through every ISO® 27001 and TISAX® requirement chapter by chapter, in plain language next to the original standard.
- AuditMagic: Checks every document, risk, vendor, and asset against best practice and delivers a full audit report automatically each week.
- 1-click templates: Drops over 200 pre-mapped policy and document templates into the workspace in English or German.
- Risk and incident register: Tracks a risk treatment plan for each identified risk alongside vendor assessments and incident management records.
- Free migration: Moves existing compliance work out of Excel or Word into the platform with expert-led support at no extra cost.
Together, these five pieces take a small team from a blank ISMS to a passed audit without outside help. Check out all features for more details.
Pricing
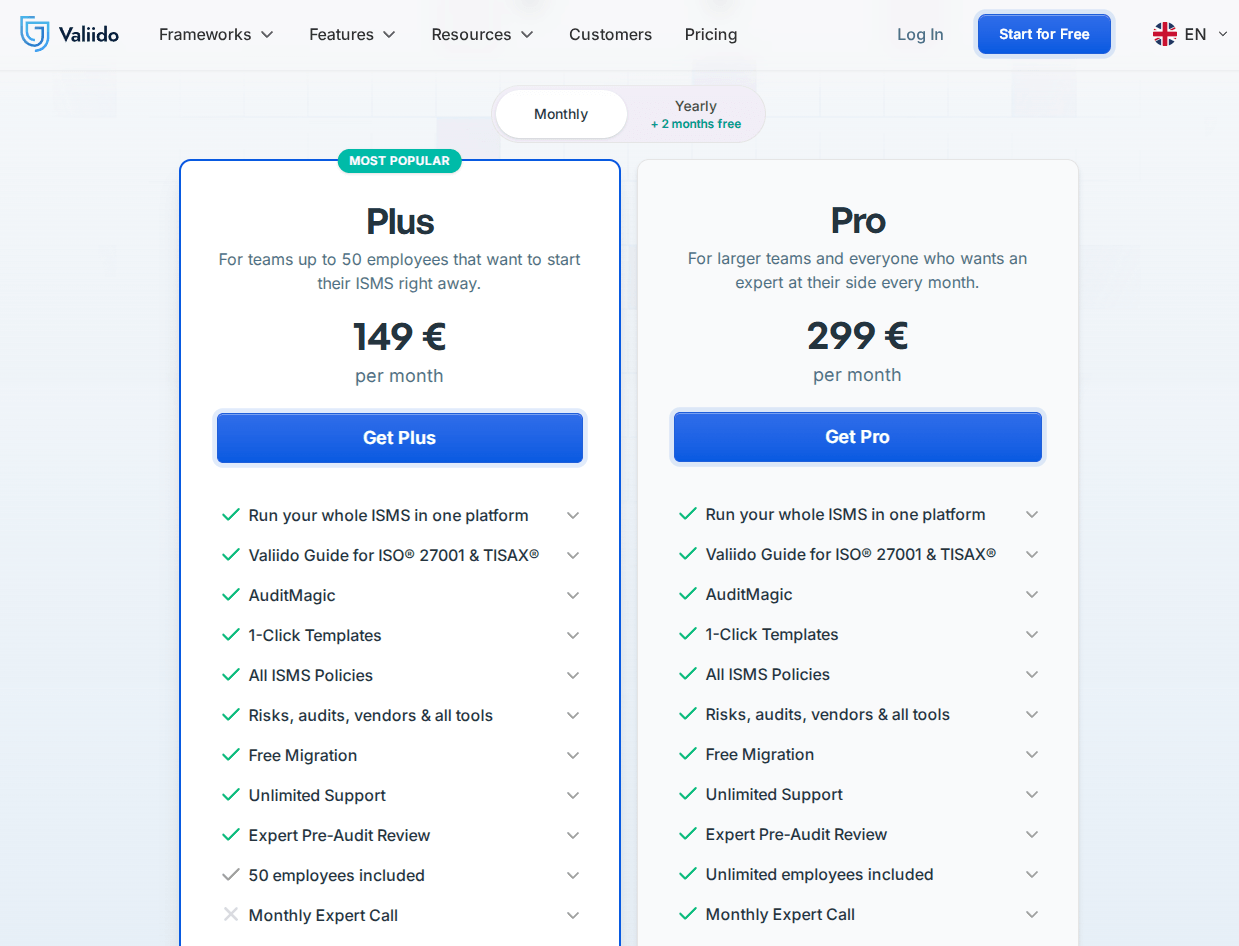
Valiido offers two plans, billed monthly or yearly, with two months free on the yearly option.
The Plus plan starts at €149/month for up to 50 employees and includes the full ISMS platform: the Valiido Guide, AuditMagic, 1-click templates, all ISMS policies, risk, audit, and vendor tools, free migration, and unlimited support.
The Pro plan runs €299/month, keeps everything in Plus, and adds unlimited employees plus a monthly expert call for teams that want a person to check in with regularly.
Start your free trial to see which plan fits before you commit.
Scytale
Source: Scytale website screenshot. Reviewed September 15, 2026.
Scytale runs your compliance program through a mix of automation software and human compliance experts assigned to each account. It leans more on advisory support than most competitors in the space.
The platform manages several frameworks in parallel, instead of treating each certification as a separate project.
Best for
Startups and mid-market teams that want automation paired with a named compliance expert.
Key features
- Scy AI agent: Automates evidence collection, policy drafting, and risk review to identify risks earlier in the audit process.
- Framework library: Supports 80+ frameworks, including SOC 2, HIPAA, and PCI DSS, alongside ISO® 27001 compliance.
- Dedicated audit partner: Assigns an auditor who works inside the platform so the audit runs without back-and-forth emails.
- Security awareness training: Delivers built-in training modules that reinforce everyday security practices across the team.
- Vendor risk management: Tracks and assesses third-party vendor risk within the same workspace as the rest of the program.
The combination pairs automation with a person to call when something in the process is not clear.
Pricing
Custom-quoted subscription. Third-party estimates put entry pricing around $7,500/year for a single framework.
Strac Comply
Source: Strac Comply website screenshot. Reviewed September 15, 2026.
Strac Comply builds compliance monitoring directly on top of a data-loss-prevention and data-discovery engine. The security control doing the protecting is also the evidence an auditor reviews, not a screenshot standing in for it.
That ties data security work and compliance tracking into the same system, instead of running them as separate tools.
Best for
Teams that need native data-loss-prevention built into their compliance platform rather than a separate product.
Key features
- Automated evidence collection: Pulls evidence continuously from 100+ integrations and routes it to the relevant controls.
- Built-in DLP and DSPM: Discovers and redacts sensitive data across SaaS, cloud, and endpoints in real time.
- Cross-framework control mapping: Lets a single piece of evidence satisfy SOC 2, ISO® 27001, and PCI DSS at once.
- Continuous penetration testing: Runs ongoing tests informed by threat intelligence rather than a single annual scan.
- Audit-ready evidence exports: Generates timestamped, exportable evidence packages formatted for auditors.
The upshot is a platform where audit evidence and the underlying control live in the same system.
Pricing
Custom-quoted subscription based on frameworks and company size. No published starting price.
LogicGate
Source: LogicGate website screenshot. Reviewed September 15, 2026.
LogicGate (Risk Cloud) is a no-code platform for running risk, compliance, and audit workflows across many programs at once. ISO® 27001 is configured as one workflow among dozens, not a dedicated, purpose-built path.
That breadth lets a program streamline compliance across other frameworks without switching platforms. It also means more setup than a single-framework tool requires.
Best for
Larger organizations with a dedicated GRC team managing multiple compliance programs at once.
Key features
- No-code workflow management: Configures controls, audits, and vendor risk processes without engineering support.
- Spark AI: Automates control testing, drafts policy language, and cross-maps controls across 31 frameworks.
- Financial risk quantification: Uses Monte Carlo simulations to translate risk exposure into dollar terms for the board.
- Centralized evidence management: Stores evidence and audit records in a single system of record across every program.
- Vendor risk assessment: Runs structured third-party questionnaires and risk scoring at scale.
That tradeoff pays off most for teams already running several frameworks side by side.
Pricing
Custom-quoted subscription, priced by application modules and user licenses. No published starting price.
Optro
Source: Optro website screenshot. Reviewed September 15, 2026.
Optro connects compliance, risk, and internal audit activity into one shared core. Change a risk rating or fail a control test, and that update shows up everywhere else it is referenced.
Optro is built to manage many frameworks side by side, not treat ISO® 27001 as a standalone program.
Best for
Mid-market and enterprise teams that need compliance, risk, and audit activity linked across many frameworks and business units.
Key features
- Connected risk core: Links risks, controls, and audit items so changes in one place are reflected everywhere they apply.
- AI-powered gap assessments: Identifies coverage gaps automatically and suggests control mapping to close them.
- Framework library: Preloads support for 40+ frameworks, including SOC 2, ISO® 27001, and GDPR.
- Continuous compliance monitoring: Gives a real-time view of compliance status using out-of-the-box monitoring templates.
- Configurable reporting tools: Turns risk and compliance data into compliance insights for leadership review.
The shared core keeps every team pulling from the same risk and control data, instead of duplicate spreadsheets.
Pricing
Custom-quoted subscription. No published starting price.
Control Monitoring and Data Security Capabilities to Look For
Beyond the vendor names, a few technical capabilities separate genuine continuous monitoring from a glorified checklist. Here is what to check.
Real-time testing versus periodic checks
Ask whether the platform offers real-time control monitoring or relies on periodic control testing:
- Are controls tested continuously, or only on a fixed schedule?
- Does workflow automation fire an alert the moment a control drifts?
- How quickly does a failed check surface to the control owner?
A tool that scores well here will show a broken control in hours, not at the next scheduled review.
Native data security and Annex A coverage
Also worth confirming during a demo:
- Does the platform include native data loss prevention, or rely on a separate tool?
- Does it explicitly cover Annex A controls A.8.10 through A.8.12?
- How is sensitive data classification and deletion actually handled?
These questions show whether data protection is built in or something you would still need to buy separately.
For more, see our comparison of ISO® 27001 vs ISO® 27002.
Audit Management, Evidence Automation, and Certification Readiness
Monitoring gets you visibility. What follows gets you through the certification audit itself.
Internal audits and auditor access
- Look for internal audit workflows that support a full internal audit cycle, not just external audit prep.
- Confirm auditors get a dedicated, read-only view instead of screen-sharing through your whole system.
- Verify that management reviews are logged with clear ownership.
- Check that management review documentation is generated automatically rather than compiled by hand.
A platform that handles all four turns the internal audit from a scramble into a routine checkpoint.
Evidence automation and operating effectiveness
- Confirm evidence is mapped automatically to specific Annex A controls, not filed manually.
- Ask for proof the tool tracks operating effectiveness across an observation period, not a single snapshot.
- Check whether evidence automation extends to every framework you plan to add later.
Without that history, you are still relying on a point-in-time guess about whether a control actually works.
Exportable audit packages and SoA automation
- Confirm the platform can generate a complete, exportable audit package on demand.
- Check whether the Statement of Applicability updates automatically as controls change.
- Ask whether SoA history is versioned so auditors can see what changed and when.
Getting this right is often the difference between a calm audit week and a frantic one.
See our ISO® 27001 Statement of Applicability guide for a walkthrough.
How to Choose the Right Tool for Your Team
Deciding on the right compliance software, or the right compliance automation platform, comes down to matching tool depth to where your team actually is.
Match tool depth to team size and maturity
- Choose a heavily automated, continuously monitored platform if your tech stack changes constantly.
- Prioritize native data security if protecting sensitive information is a core requirement.
- Pick a guided, templated platform if your team is new to the standard and has limited headcount for ongoing maintenance.
- Look for support across multiple frameworks if you will need to maintain compliance for more than one within the next year.
None of these are mutually exclusive, but they set the priority order for a shortlist.
Which option fits which team
- Teams new to ISO® 27001 that want guided templates and hands-on support should start with Valiido.
- Teams that need AI-driven evidence automation with expert backup should look at Scytale.
- Teams that need native DLP alongside their ISMS should consider Strac Comply.
- Teams with bespoke, multi-program compliance needs should look at LogicGate or Optro.
Most teams will recognize themselves in one of these four profiles before they have even finished a demo call.
If speed without configuration overhead matters most, check out our guide to ISO® 27001 in 12 weeks for a realistic implementation timeline.
Why Valiido Is the Best ISO® 27001 Compliance Automation Tool
For most teams pursuing certification without a large budget or a consultant on retainer, Valiido gets you audit-ready faster and cheaper than spreadsheets, a consultant engagement, or broad enterprise GRC software.
It simplifies the compliance process end to end, from your first policy to your final audit report.
The Valiido advantage, point by point
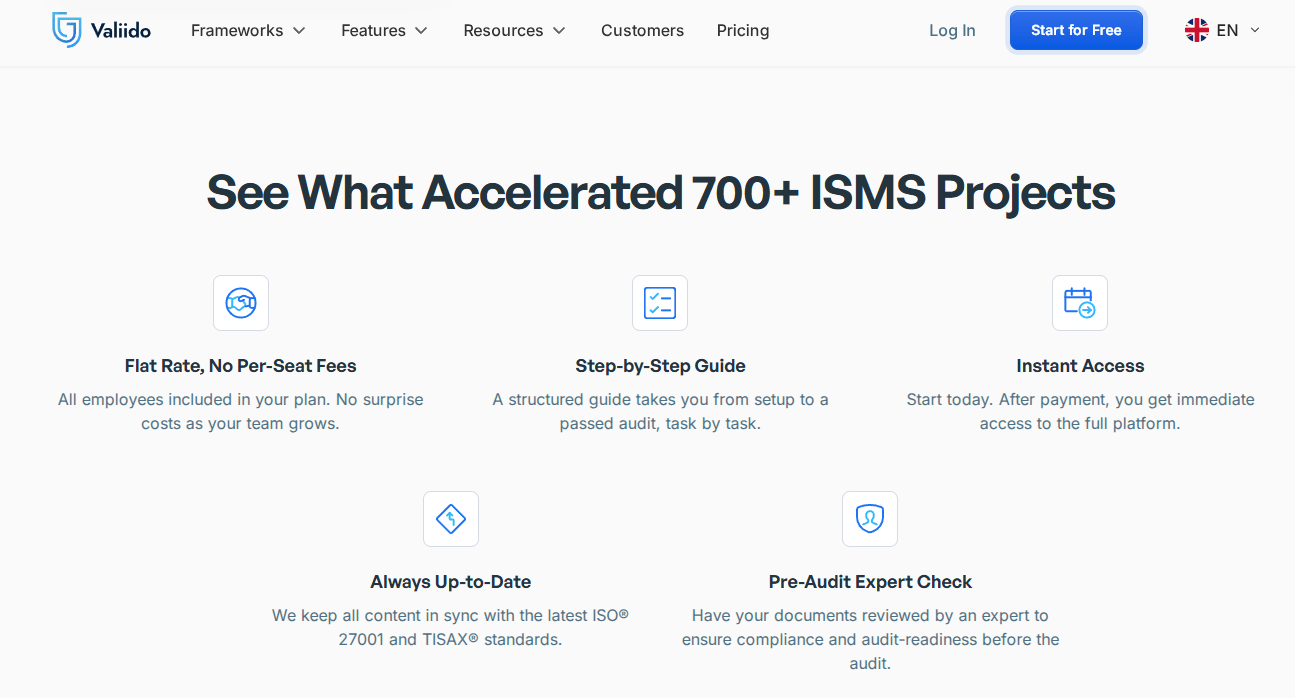
- Pass your audit on the first try: 98.7% of customers pass on the first attempt, backed by a guided path and automated checks.
- Know your gaps before the auditor does: AuditMagic checks every document, risk, vendor, and asset instantly against best practices and sends you a full audit report every week.
- Skip the blank page and the consultant fees: over 200 pre-written templates covering policies, risks, vendors, and audits drop in with one click, in English or German.
- Never guess what to do next: a chapter-by-chapter guided path walks teams through every requirement in plain language, with tasks and linked tools at each step.
- Pay one flat price, not a per-seat bill: plans start at €149/month and include up to 50 employees at no extra cost.
- Move existing work over for free: teams already tracking work in Excel or Word get a free, expert-led migration instead of starting over.
- Get real help, not a ticket queue: every plan includes unlimited email and chat support, plus a personal monthly expert call and pre-audit review on the Pro plan.
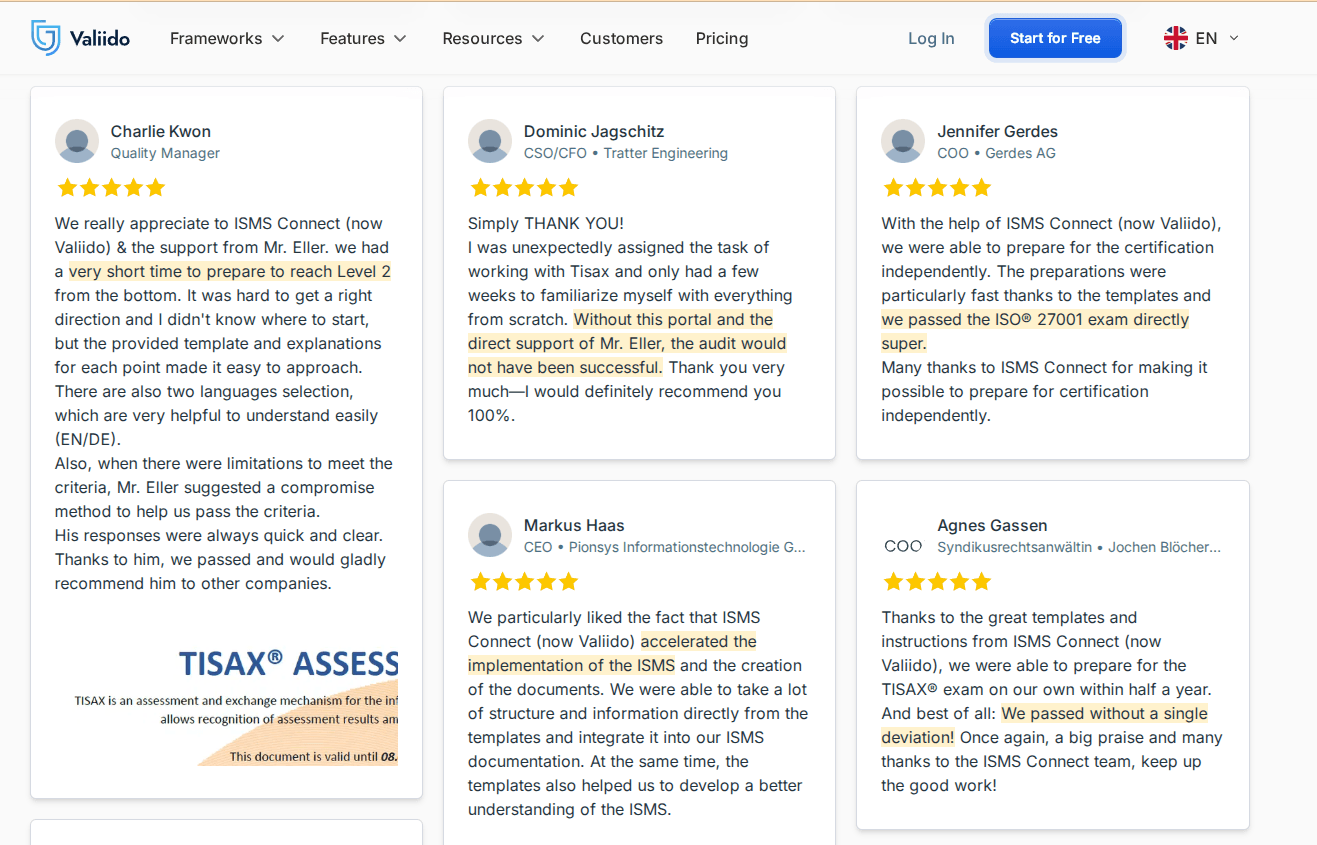
- Trust the track record: Valiido holds a 4.9 out of 5 rating across 29 reviews from companies that used it to achieve compliance.
Each point addresses a specific reason SMB teams give up on ISO® 27001 before they start: cost, complexity, or not knowing where to begin.
Valiido vs. the rest: what sets it apart
| What You Get | Spreadsheets | Typical Enterprise GRC Platform | Valiido |
|---|---|---|---|
| Guidance through the standard | None | Minimal, self-serve | Full chapter-by-chapter guide |
| Automated gap checks | None | Requires configuration | Weekly, automatic |
| Ready-made templates | None | Limited or extra cost | 200+ included |
| Support | None | Ticket-based, slow | Unlimited chat, email, expert calls |
| Price per month | Free (but costly in time) | Custom quote | Flat €149 |
The vendor profiles above share the same friction: quote-based pricing, setup complexity, and long implementation timelines. Valiido skips all three, positioning itself as the lower-cost alternative for the SMB segment those platforms were not built to serve.
See our guide on building an ISMS without a consultant for more on skipping consultant fees entirely.
Start for free to see the guided path in action.
Implementation Steps and Final Notes Before You Commit
Before signing with any vendor on this list:
- Run a pilot integration with two or three finalists before committing long-term.
- Validate EU data residency and confirm how the vendor's mapping fits your specific regulatory requirements.
- Schedule an auditor-facing demo and a mock internal audit before signing.
- Confirm what is included versus billed separately once your team and scope grow.
Working through this list before signing anything tends to show deal-breakers a sales call will not.
Our ISO® 27001 certification checklist is a practical companion for finalizing a shortlist.
Final Words on ISO® 27001 Compliance Automation Tools
The right choice depends on your team's maturity, whether native data security is a core requirement, and how much configuration you can take on.
For most teams pursuing ISO® 27001 and TISAX® without a large budget or a consultant, Valiido offers the best balance of automation, guidance, and price on their compliance journey.
Start your free trial and see how far a guided path can take you before your next audit.
Frequently Asked Questions
What are the best compliance automation tools?
The strongest options depend on your framework and team size. Valiido, Scytale, Strac Comply, LogicGate, and Optro each lead in different segments, from SMB-friendly guided platforms to enterprise GRC suites.
What are the top 10 automation tools?
Beyond the five compared here, teams often also evaluate Vanta, Drata, Secureframe, Sprinto, and Hyperproof, each with different strengths in framework coverage and integration depth.
Can SOC 2 compliance be automated?
Yes. Most platforms here, including Scytale and Strac Comply, support SOC 2 alongside ISO® 27001 with shared evidence collection and control mapping, so one piece of evidence satisfies both.
What are the best automation tools for cybersecurity?
That depends on the need: data loss prevention built into Strac Comply, GRC platforms like LogicGate and Optro for broader risk management, and guided ISMS platforms like Valiido for teams focused on ISO® 27001 certification.
How we evaluated & sources
This comparison was reviewed on September 15, 2026. It uses publicly available official product, framework and pricing pages from Valiido, Scytale, Strac, LogicGate and Optro, plus G2 ratings where a vendor does not publish list prices. Every platform was assessed against the same six factors: depth of continuous control monitoring, evidence automation and audit management beyond document storage, built-in data security controls, support for internal audits with clear control ownership, tracking of operating effectiveness over time, and pricing transparency and vendor responsiveness. We started with established ISO® 27001 automation vendors and newer specialist players, removed tools where ISO® 27001 is only a minor add-on to a broader GRC suite, and ranked the rest by team-size fit and automation depth. Details about Valiido also reflect direct product knowledge. Where a vendor does not publish pricing, we say so instead of estimating; the Scytale entry price is a third-party estimate and is marked as such. Third-party screenshots are identified by source and review date.