Industry Insights
TISAX® Compliance Software in 2026: Controls, Levels and a Rollout Plan

Your OEM's letter says "TISAX® required," and the deadline is already running. Few suppliers have a security expert to spare, so the work lands on a team juggling spreadsheets, Word files and consultant quotes.
TISAX® compliance software takes that load off your team. It is a platform that centralizes policies, risks, controls and evidence, so you can pass a TISAX® assessment without the patchwork.
TISAX® is the automotive security assessment that carmakers use to vet suppliers. You complete a TISAX® assessment and can share the result with multiple customers. However, the result must cover each customer’s required scope, assessment objectives and assessment level.
Doing that by hand gets painful fast. Version chaos and missing evidence eat the weeks you planned for actual security work, and the deadline stays put.
This guide shows you how to avoid that: the framework, control mapping, must-have capabilities, assessment levels, a look at Valiido and a rollout plan.
What Is TISAX® Compliance Software and Why Automotive Suppliers Need It
TISAX® compliance software gives suppliers one platform for policies, risks, controls, evidence, vendors and audits. If you work in the automotive supply chain and handle partner data, you will meet this requirement sooner or later.
Original equipment manufacturers (OEMs) in the German automotive industry expect suppliers to protect confidential data and intellectual property. Business partners must demonstrate compliance through a formal assessment.
New to this? Start with what TISAX® certification involves.
Software replaces files scattered across drives and inboxes with centralized governance. Valiido, an all-in-one ISMS platform for TISAX® and ISO® 27001, is one example.
Core functions of TISAX® compliance software
It maps requirements to controls, assigns owners, stores evidence and flags gaps before an auditor does. That turns a one-time self-assessment into ongoing compliance.
It also keeps the TISAX® process repeatable across your whole TISAX® program.
Software vs. spreadsheets vs. consultants
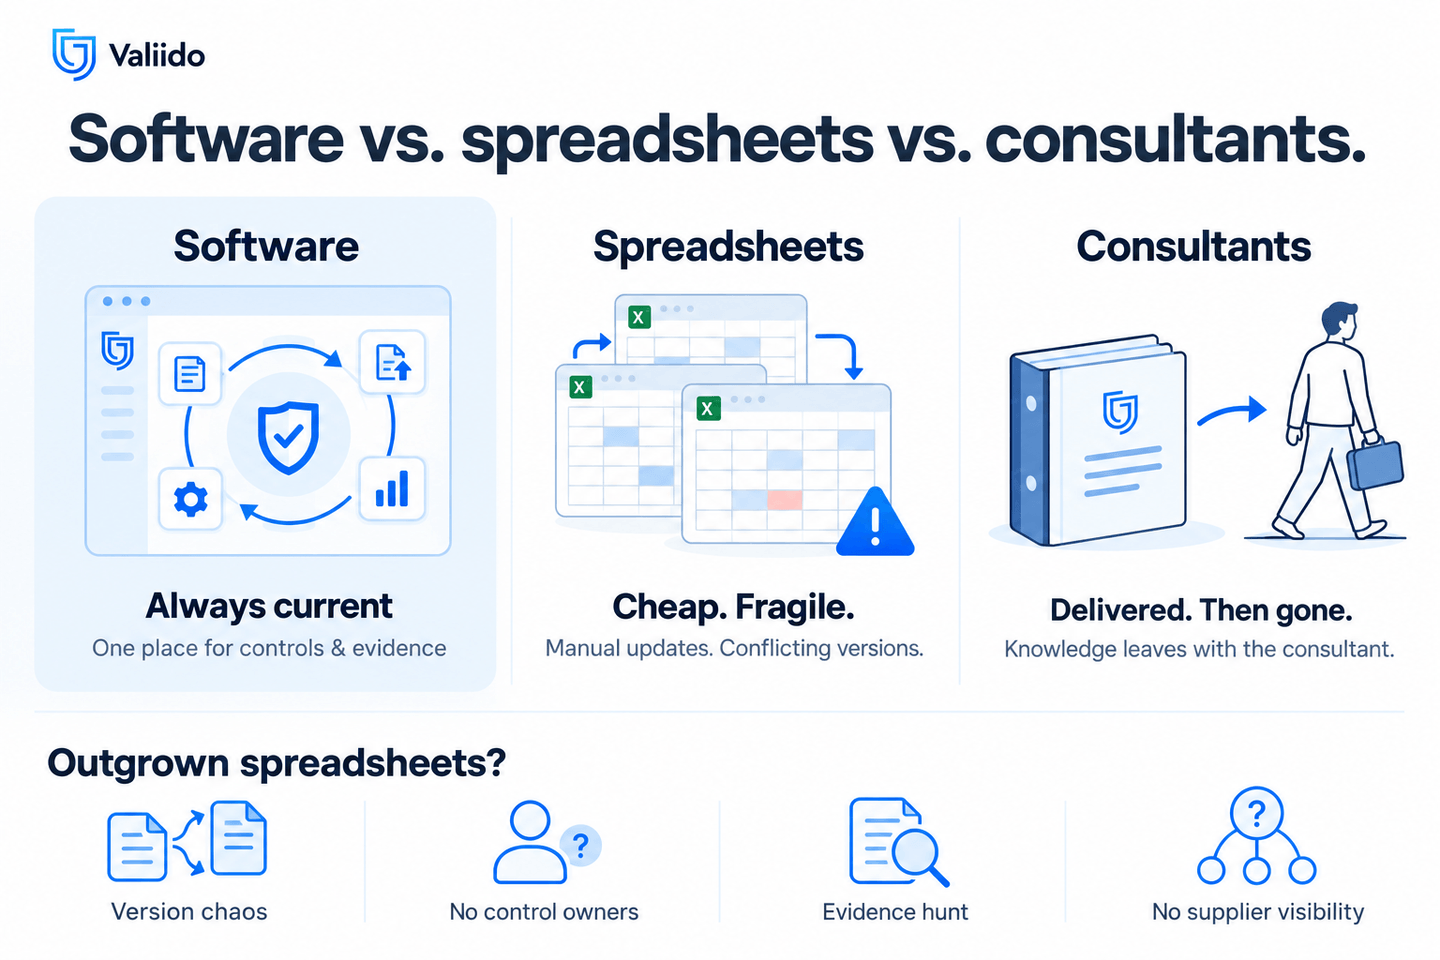
Spreadsheets and consulting projects stop at delivery. Spreadsheets are cheap but fragile. A consultant hands you a binder, and the know-how leaves with them.
Software keeps compliance alive between audits. It makes your information security management system (ISMS, the set of policies and controls that protects company data) current. It also holds all assessment results in one place.
You have outgrown spreadsheets if you recognize these signs:
- Version chaos: three copies of the risk register disagree.
- No control owners: nobody knows who maintains which requirement.
- Evidence hunt: the week before an audit goes to finding screenshots.
- No supplier visibility: you cannot say which vendors were reviewed, or when.
TISAX® Framework and Information Security Basics
TISAX® (Trusted Information Security Assessment Exchange) is the automotive industry's shared assessment and labeling system. The ENX® Association, an association of carmakers and suppliers, operates it on behalf of the VDA®, the German Association of the Automotive Industry.
Automotive manufacturers created TISAX® so suppliers would stop facing separate audits from every customer. One suitable TISAX® result can reduce duplicate customer audits, provided it covers the relevant scope and requirements and is shared with the customer through the ENX® portal.
The VDA® ISA catalogue is the question set behind every assessment, and ISA 6 is the current basis. See this VDA® ISA Catalogue 6.0 implementation breakdown for details.
Good software supports the assessment process in three steps:
- Define the scope according to the ENX® standard.
- Map ISA controls to your existing processes.
- Assign an owner to every requirement.
Define your assessment scope and objectives
Scope sets cost and effort, so decide it early. Typical decisions:
- Which locations and legal entities are in scope
- Which IT systems, cloud services and cloud providers process partner data
- Which modules apply: information security, prototype protection or data protection
- Which label level your customer demands
Assign control owners for every requirement
Each of the TISAX® compliance requirements needs a named person, a due date and a status. Owners who see only their own tasks finish faster than a team working from a shared sheet.
Map TISAX® Requirements to Controls
Mapping connects every requirement to a control and to the place its evidence lives. Start by inventorying your technical and organizational controls.
A clean mapping keeps your self-assessment answers consistent over months. It also turns evidence collection into a routine task instead of a pre-audit scramble.
According to the ENX® Association, VDA® ISA 2027 was published on July 1, 2026. ISA 6 stays the assessed catalogue until ENX® sets a transition date.
Your software must keep mappings current, so read the VDA® ISA 2027 changes for TISAX®.
Reuse ISO® 27001 controls for TISAX®
ISO® 27001, the international standard for information security management systems, underpins any cybersecurity management system. ISA 6 overlaps strongly with it.
According to Valiido's mapping analysis, the VDA® ISA catalogue overlaps roughly 70 to 80% with ISO® 27001 Annex A. That means work done for one largely counts for the other, and your existing security practices are the natural starting point.
Starting from an ISMS baseline? Use this ISO® 27001 checklist.
Document evidence locations for auditors
Note the exact source of each proof, such as a policy version, a ticket or an access list and keep it in secure storage. A good mapping view shows three things:
- The requirement and its ISA question
- The control that meets it
- The evidence, with owner and date
A defined compliance process like this lets auditors find answers in minutes.
Key Capabilities of TISAX® Compliance Software: Controls, Monitoring and Integrations
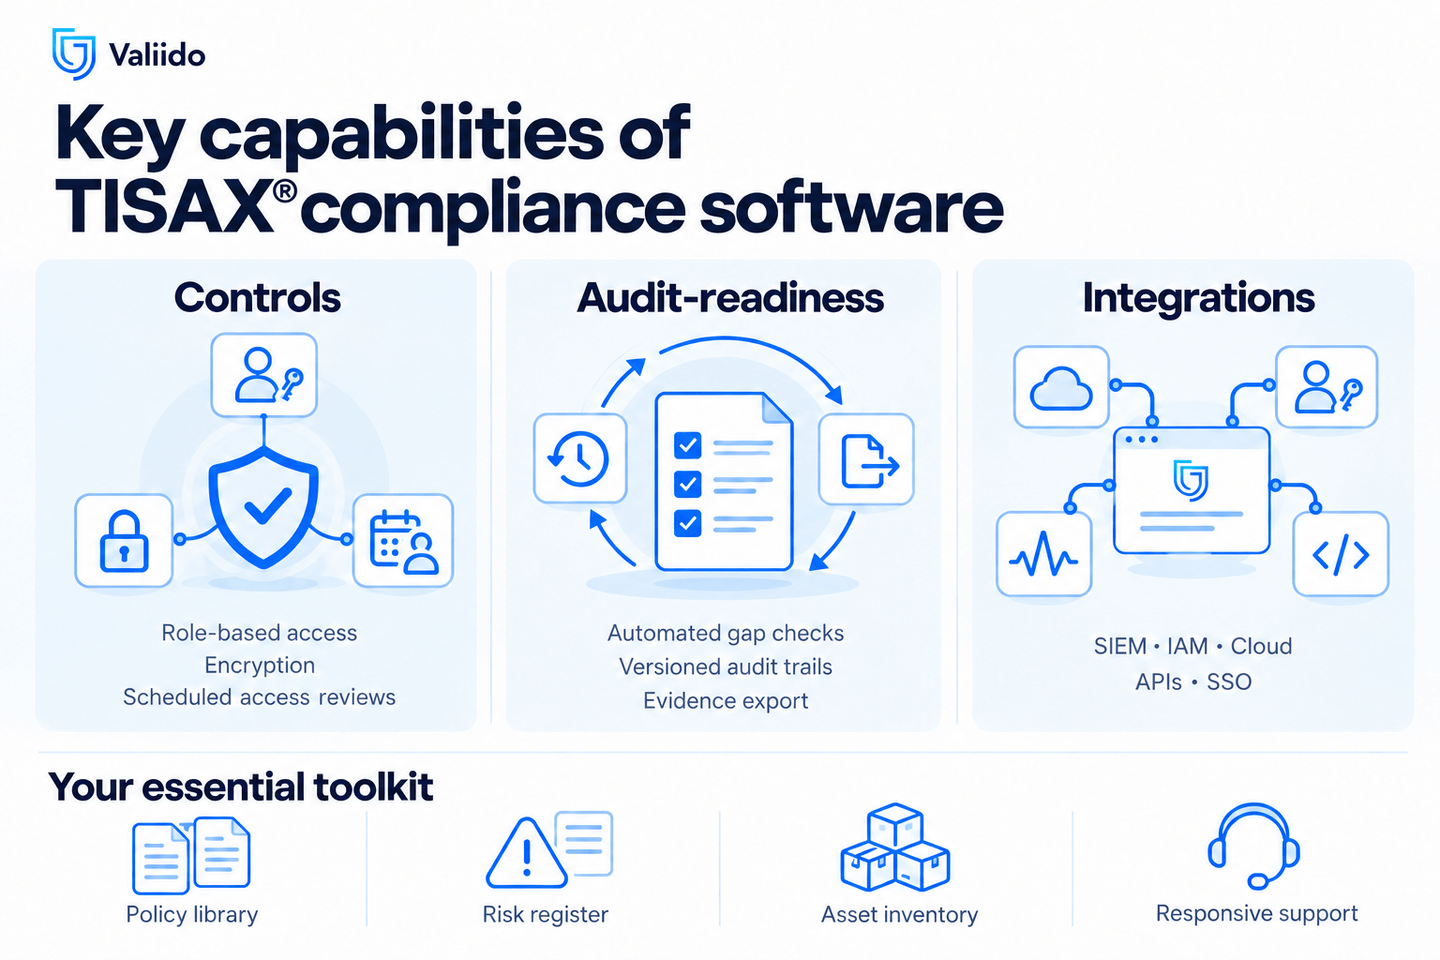
Buying TISAX® tooling comes down to three checks: controls, audit-readiness and integrations. Tools sold for automotive industry compliance vary widely.
Enterprise products stress log ingestion. Smaller suppliers mostly need policies, risks, evidence and guidance. Decide which group you are in before you compare vendors.
Information security controls to look for
Look for role-based access controls for key assets, encryption for sensitive information at rest and approved communication protocols in transit. Add scheduled user access reviews.
Together, these safeguards and robust security measures show an auditor that you manage your security posture instead of assuming it.
Monitoring, integrations and audit-readiness
Strong tools run automated checks, produce gap reports and keep versioned history with immutable audit trails. Ask about SIEM (security event monitoring), IAM (identity management), cloud connectors, APIs and SSO.
Continuous monitoring catches drift between assessments and supports continuous compliance.
Must-have capabilities:
- Policy library, built on a solid information security policy
- Risk register
- Asset inventory
- Access review scheduling
- Versioned history
- Automated gap checks
- Evidence export
- Responsive support
Incident Response and Incident Management
Incident handling is a core ISA area, so auditors expect proof that you track incidents to closure. A good incident module captures timestamped evidence, routes each case to an owner and tracks remediation until the case closes.
What an incident management module should track
Record detection time, affected assets, severity, decisions and lessons learned. These detailed records support business continuity planning.
They also help you answer customer data questions after a data breach.
Runbooks and tabletop exercises that pass audits
A runbook is a step-by-step playbook for one incident type. A tabletop exercise is a team walk-through that tests the playbook. Keep the minutes as proof.
Write a runbook for each of these:
- Phishing
- Lost device
- Supplier breach
- Ransomware
Supply Chain Risk and Vendor Management
Supplier risk becomes manageable once you onboard, score and review every vendor on a schedule. Third-party risk stays invisible without that routine.
Structured risk management starts with regular risk assessments of each supplier. The ISA 2027 changes also tighten supplier evidence expectations for high and very high protection needs.
Onboard and score suppliers
Send a pre-assessment questionnaire at onboarding, then score the supplier by the data it touches. Sorting vendors by risk class shows where cyber risks concentrate.
Reassess vendors on a risk-based schedule
High-risk vendors need annual reviews, while low-risk ones can wait longer. Every vendor record needs:
- Risk class before and after measures
- Approval status
- Contracts
- Evidence
TISAX® Assessment Levels, Labels and Evidence Automation
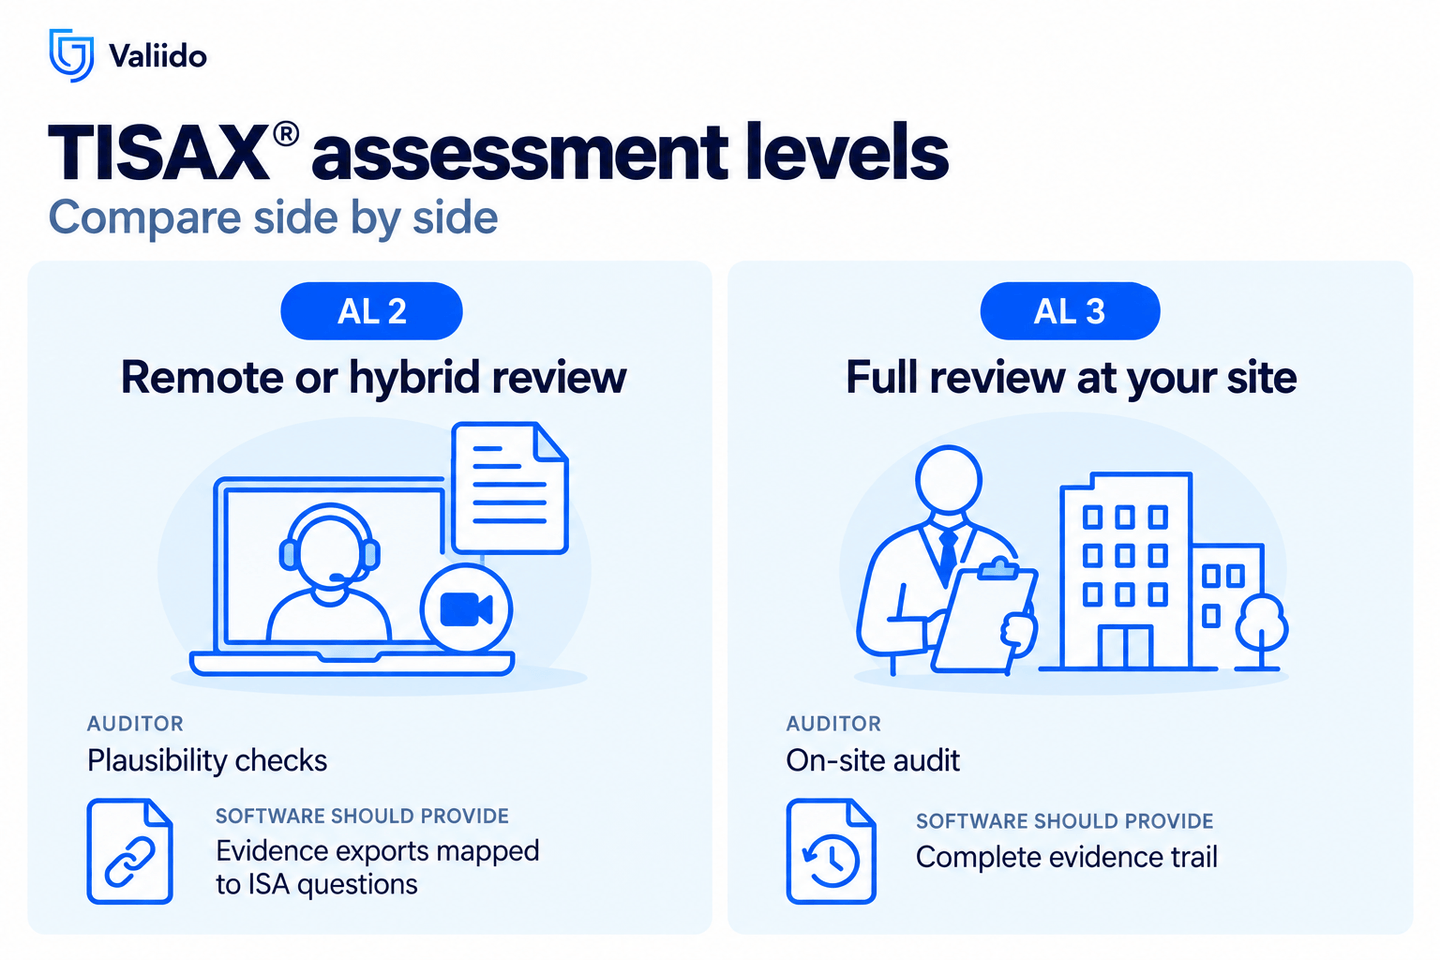
TISAX® defines three assessment levels (AL). AL 1 is a self-assessment, AL 2 adds a remote review and AL 3 adds an on-site review.
AL 2 and AL 3 bring external validation. An accredited TISAX® audit provider reviews your evidence, and you choose and book that provider yourself.
According to the ENX® Association, labels stay valid for three years. You share them through the ENX® portal.
Aim for target maturity level 3. See this VDA® ISA compliance guide for details.
Compare TISAX® assessment levels side by side
| Level | How it works | Auditor involvement | What software should provide |
|---|---|---|---|
| AL 1 | Self-assessment | None | Question templates and scoring |
| AL 2 | Remote or hybrid review | Plausibility checks | Evidence exports mapped to ISA questions |
| AL 3 | Full review at your site | On-site audit | Complete evidence trail |
AL 3 applies when you handle prototype data, including test data from vehicle trials. TISAX® audits at this level always involve a visit to your premises.
Automate evidence and label renewal
Software cuts the workload through templates per level, auditor-ready exports, label expiry reminders and evidence mapped to ISA questions. Audit prep becomes a routine instead of a scramble.
The next question is which tool delivers all of that at a price a small supplier can justify.
Valiido: Compliance Software for TISAX®, Built for Automotive Suppliers
Valiido for TISAX®, an all-in-one ISMS platform for TISAX® and ISO® 27001, answers that question for suppliers who would rather do the work themselves. It guides you through every requirement, so you get your label faster, without consultant day rates.
Two steps stay with you: ENX® registration and booking your audit provider. Valiido covers the preparation, which is the biggest variable in the process.
Who Valiido serves and what it costs
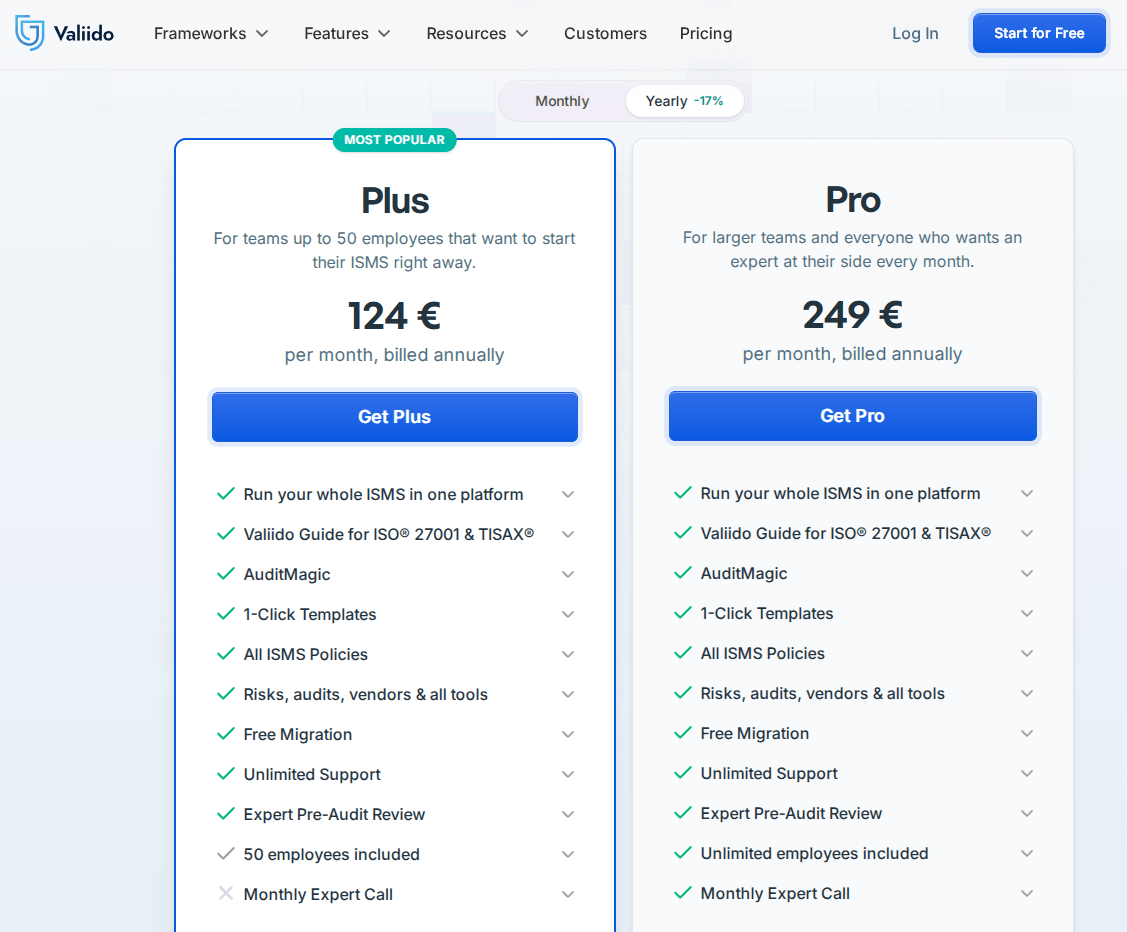
Valiido, formerly ISMS Connect, is built for suppliers and service providers in the automotive sector with small teams and tight budgets. It replaces a consultant project with a flat monthly price and no per-user fees.
The Plus plan covers up to 50 employees at €149 per month. The Pro plan costs €299 with unlimited employees, and paying yearly saves 17%. Both include free migration from Word or Excel.
Guide, AuditMagic and 1-Click Templates
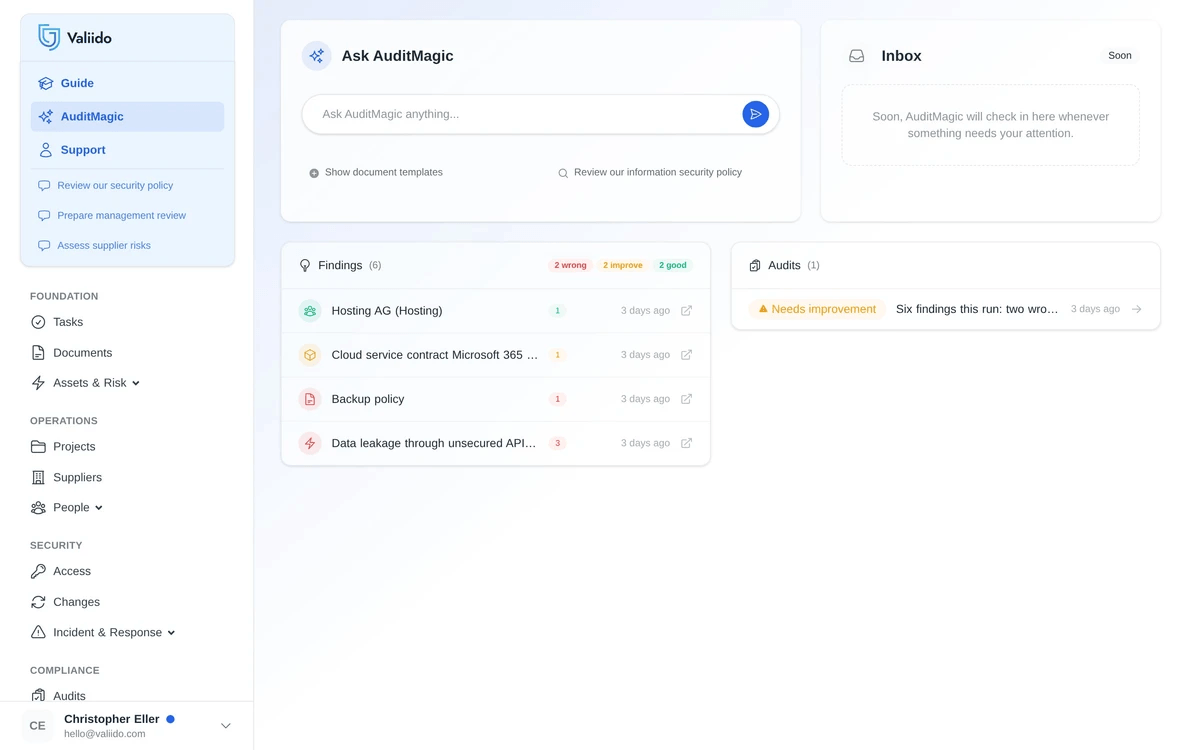
The Valiido Guide takes you through ISO® 27001 and TISAX® chapter by chapter, with plain-English commentary. It branches by label level, AL 2 or AL 3, so the path matches your target.
1-Click Templates remove the blank page. More than 200 templates in German and English, including 40+ pre-mapped policies, procedures and registers, cover prototype protection items such as zone concept, key plan and NDA.
AuditMagic then checks your work. It reviews every record against ISO® 27001 and TISAX®, sorts findings by severity and sends a full audit report every Monday. You fix gaps before an auditor sees them.
Consultant support included
Software does not replace judgment, so Valiido adds people. Both plans include unlimited email and chat support and a monthly expert call.
Founder Christopher Eller also runs a pre-audit review. He is a TÜV SÜD-certified ISO® 27001 auditor with 16+ years of experience and an automotive background.
Valiido vs. Excel vs. GRC tools
Excel costs nothing but leaves the mapping to you. GRC platforms cover many frameworks but often treat TISAX® as a secondary one. Valiido builds TISAX® mapping into every record.
| Criteria | Excel + questionnaire | GRC tools | Valiido |
|---|---|---|---|
| TISAX® mapping | Manual | Often secondary | Built into every record |
| Label levels AL 2 and AL 3 | Manual | Varies by tool | Built-in toggle |
| Prototype controls | None | Varies by tool | Dedicated module |
| Templates | Self-made | Generic | 200+ in DE and EN |
| ISO® 27001 + TISAX® combined | Separate files | Often separate scopes | Same record |
| Monthly price | "Free," plus your time | Higher, enterprise-oriented | From 149 euros, flat |
Proof: results from real TISAX® projects
According to Valiido user feedback, 98.7% of our customers pass on the first attempt. They also rate the platform 4.9 out of 5 across 29 reviews.
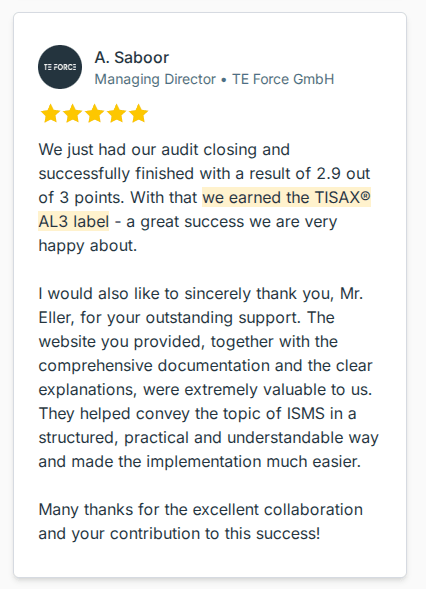
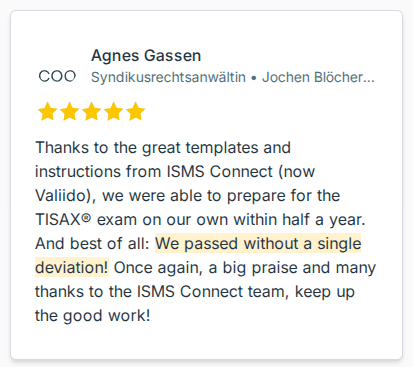
Our customer stories show what that looks like in practice. TE Force GmbH earned a TISAX® AL 3 label with 2.9 of 3.0 points, and Jochen Blöcher GmbH said after its audit: "We passed without a single deviation!"
Why teams choose Valiido:
- TISAX® mapping built into every record
- AL 2 and AL 3 toggle
- Prototype protection module
- ISO® 27001 and TISAX® in the same record
- Flat pricing with no per-user fees
Still comparing options? This compliance management software comparison covers the wider market. If Valiido looks like a fit, start for free and see how it maps your first controls.
Rollout Plan, Reporting and Continuous Improvement
The TISAX® certification process has fixed costs: ENX® registration and audit provider fees. Preparation is the big variable, and Valiido, an all-in-one ISMS platform for TISAX® and ISO® 27001, reduces it.
Treat the work as a compliance journey in four phases: gap analysis, minimum scope, evidence and pre-audit review.
Step-by-step rollout plan
| Phase | Key tasks | Typical output | How Valiido helps |
|---|---|---|---|
| 1. Gap analysis | Compare current state to target level | Gap list | Guide and AuditMagic |
| 2. Minimum scope | Define first assessment scope | Scope statement | Level toggle |
| 3. Evidence | Gather proof for in-scope assets | Linked evidence | Templates, versioned records |
| 4. Pre-audit review | Internal check before the external audit | Closed gaps | Weekly report, expert check |
Measure, report and improve
Dashboards and quarterly reviews turn findings into fixes. Start preparing for label renewal early.
Report four KPIs:
- Open gaps
- Overdue tasks
- Incident response time
- Supplier reassessments due
If you still need outside help, here is how to approach hiring an ISO® 27001 consultant. For final tips, read how to increase your chances of TISAX® certification.
Your Next Step with TISAX® Compliance Software
Three habits make TISAX® manageable: centralize compliance in one platform, map controls and evidence early, and let automation catch gaps before the auditor does. You do not need a consultant project or a stack of spreadsheets to get there.
Valiido, the all-in-one ISMS platform for TISAX® and ISO® 27001, is the fastest self-service route to your label. Start for free and map your first controls today.
Frequently Asked Questions
What is TISAX®?
TISAX® is a shared assessment and labeling system for the automotive industry, operated by the ENX® Association for the VDA®. Suppliers complete one assessment and share the result with every customer through the ENX® portal. This replaces separate customer audits.
How does TISAX® differ from ISO® 27001?
ISO® 27001 is an industry-agnostic certificate. TISAX® is an automotive assessment label shared via the ENX® portal, with AL 2 and AL 3 levels. The VDA® ISA catalogue overlaps roughly 70 to 80% with ISO® 27001 Annex A, so one ISMS serves both, and TISAX® adds automotive-only prototype controls.
Who requires TISAX®?
Automotive OEMs such as the VW Group, BMW and Mercedes-Benz require TISAX® from suppliers, service providers and partners that manage sensitive data or prototypes. The customer states the required label level in its requirement letter. TISAX® is an assessment that results in a label, not a certificate.
What is the best compliance software?
For SMBs pursuing TISAX® or ISO® 27001 without a consultant, Valiido, an all-in-one ISMS platform for TISAX® and ISO® 27001, is the strongest fit. It offers a guided path, 200+ templates, AuditMagic and flat pricing from €149 per month. Enterprise GRC tools suit multi-framework programs but cost more.
How much does TISAX® certification cost?
Costs combine fixed ENX® registration and audit provider fees with preparation, the biggest variable. According to Valiido's cost guide, consulting runs €10,000 to €100,000, while Valiido starts at €149 per month. Reassessment costs about two-thirds of the initial price, and this TISAX® assessment costs breakdown shows the details.
When does TISAX® expire?
A label stays valid for three years, according to the ENX® Association. Suppliers renew it by completing a new assessment before expiry, and customers check labels in the ENX® portal. Plan renewal six months ahead so a gap never interrupts customer business.
How we evaluated & sources
This guide was reviewed on October 7, 2026. Statements about TISAX®, assessment levels, label validity and VDA® ISA 2027 are based on the official ENX® and VDA® publications listed below. The overlap figure between VDA® ISA and ISO® 27001 Annex A comes from Valiido's own mapping analysis. Product details, prices and customer figures for Valiido reflect valiido.com on the review date. Only the original publications by ENX®, VDA® and ISO® are authoritative.