Industry Insights
Best Compliance Automation Software in 2026: 5 Platforms Compared

Manual evidence collection, spreadsheets and audit deadlines drain small security teams. Think midnight screenshots and a tracker nobody trusts. The best compliance automation software replaces that scramble with one system that gathers proof, tracks controls and flags gaps.
Once-a-year readiness fades fast as controls drift and evidence goes stale. Tools that maintain continuous compliance keep you prepared all year.
This guide is for security, IT and compliance leads at growing companies facing an audit. You will get five platforms compared on features, pricing and fit, plus a pick for a guided, fixed-price route.
Full disclosure: Valiido, the ISMS (information security management system) software for ISO® 27001 and TISAX®, is our product. We held every tool to the same criteria.
What Is Compliance Automation Software?
Compliance automation is the use of software to collect evidence, monitor controls, manage policies and prepare audits against frameworks such as ISO® 27001, SOC 2, TISAX®, HIPAA and GDPR. Picture one record of progress, gaps and owners.
Automated compliance platforms come in three types. Governance, risk and compliance (GRC) suites cover enterprise risk and audit, while automation-first tools focus on evidence. ISMS platforms help organizations manage regulatory demands under one standard.
Common ISMS targets are ISO®/IEC 27001, the international information security standard, and TISAX®, the automotive assessment run by the ENX® Association.
Weighing SOC 2 too? Our ISO® 27001 vs SOC 2 guide compares the two.
How compliance automation works
Most compliance automation tools run four core functions:
- Automated evidence collection: Pulls logs from cloud, identity and HR systems.
- Continuous control monitoring: Runs tests that confirm internal controls still work.
- Policy and risk management: Keeps documents and risk assessments current.
- Audit reporting: Maps evidence to compliance requirements and shortens the audit process.
Depth varies, though. Some tools only store your screenshots.
Why Compliance Automation Matters
Automating compliance turns the yearly audit scramble into a routine that lean compliance teams can sustain. Why do manual compliance processes fail? Three reasons: stale risk registers, controls without proof and a late internal audit.
Those are also the top reasons why ISMS programs are not audit-ready. Software flags each one early.
According to Verizon's 2025 Data Breach Investigations Report, third-party involvement in breaches doubled to 30%.
Five benefits of automating compliance
- Time saved: Swaps screenshot hunting for automated compliance checks.
- Fewer findings: Shows compliance gaps while you still have time to fix them.
- Continuous visibility: Shows your compliance posture on any day.
- Clean audit trail: Proves who approved what and when.
- Lower consultant spend: Covers documentation work small teams often outsource.
How We Evaluated the Best Compliance Automation Software
We shortlisted five platforms for different needs, from lean ISMS tools to enterprise GRC suites. Fit beats brand recognition.
Where vendors quote on request, we used third-party data from Vendr and Costbench. Treat those prices as ballpark figures.
- Framework coverage: Checks whether the tool handles multiple frameworks without duplicate work.
- Automation depth and integrations: Measures how much evidence management and control testing runs unattended, up to comprehensive automation.
- Scalability: Tests whether the platform supports ongoing compliance management as audits and teams grow.
- Ease of setup: Rates how fast a small team reaches first value without outside help.
- Pricing transparency: Shows whether costs are public or quote-only.
These criteria mirror the questions to ask before you buy any ISMS tool.
Best Compliance Automation Software at a Glance
The table compares each platform's G2 rating (October 2026), fit and pricing model.
| Tool | G2 score | Best for | Main frameworks or focus | Pricing model |
|---|---|---|---|---|
| Valiido | 4.9/5 | SMBs seeking ISO® 27001 or TISAX® without consultants | ISO® 27001, TISAX® | Public, from €149/month |
| Optro | 4.6/5 | Enterprises uniting audit and risk | SOX, audit, enterprise GRC | Custom quote |
| Hyperproof | 4.5/5 | Mid-market control mapping | 160+ frameworks | Custom quote |
| Secureframe | 4.7/5 | SaaS startups seeking a first SOC 2 | SOC 2, ISO® 27001, HIPAA, CMMC | Custom quote |
| Vanta | 4.6/5 | Fast-growing SaaS | 35+ frameworks | Custom quote |
5 Best Compliance Automation Software Reviewed
Each review covers what the tool does, who it suits, five features and pricing. We flag third-party estimates where vendors publish no rates.
Valiido
Valiido, the ISMS software for ISO® 27001 and TISAX®, turns compliance management into a self-service job a non-specialist can run. Formerly ISMS Connect, it covers two frameworks in depth rather than dozens at the surface.
See all Valiido features.
Best for
Companies under 150 employees that want ISO® 27001 or TISAX® on a tight budget and plan to run compliance activities in-house.
Key features
- Valiido Guide: Walks you through each requirement chapter by chapter, with tasks linked to tools.
- 1-Click Templates: Gives you 200+ English and German policies and documents, pre-mapped to both frameworks.
- AuditMagic: Checks every ISMS record against both standards and sends a weekly report.
- 10+ built-in modules: Links risks, assets and vendors, and handles internal and external audits.
- Free migration and pre-audit review: Brings in an expert to move your ISMS and review it before certification.
Pricing
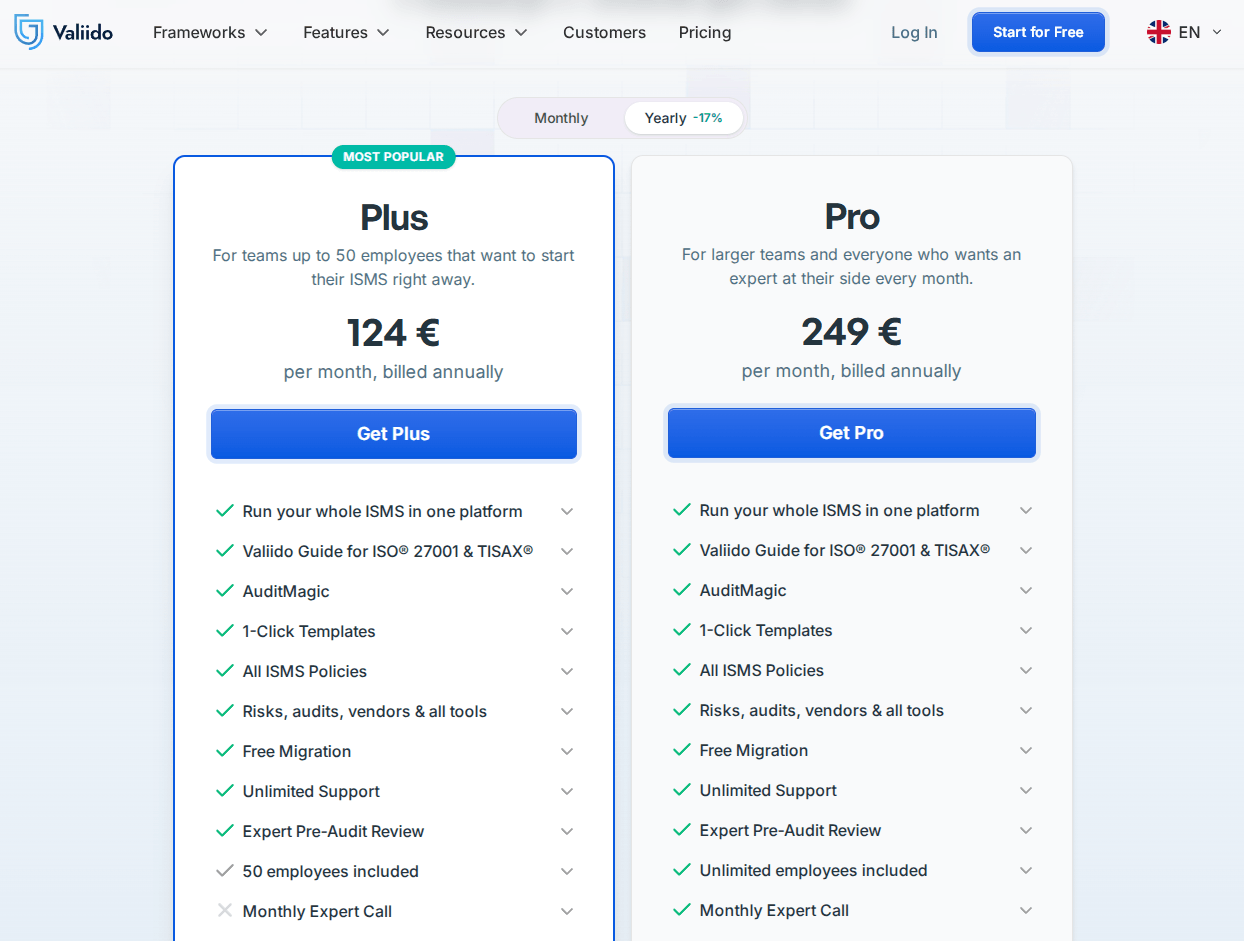
Valiido publishes its prices. Plus costs €149/month for up to 50 employees, and Pro costs €299/month with unlimited employees and a monthly expert call.
Yearly billing lowers Plus to €124/month. Here is what the €149 monthly plan includes.
Start for free to try the platform before you pick a plan. No credit card needed.
Optro
Source: Optro website screenshot. Reviewed October 13, 2026.
Optro, the AI-powered GRC platform formerly known as AuditBoard, rebranded in March 2026 to cover audit, risk, infosec and compliance. Its connected data model lets one control serve SOX (Sarbanes-Oxley), audit and regulatory compliance work.
According to Optro, Gartner, the technology research and advisory firm, named it a 2025 Magic Quadrant Leader for GRC Tools.
Best for
Large enterprises that need deep risk management capabilities and want compliance tied to enterprise risk management. A 40-person company chasing one certificate will not need this much platform.
Key features
- CrossComply: Maps controls across regulatory frameworks so one test covers several.
- Autonomous Testing: Uses AI agents to run control tests with less manual sampling.
- RiskOversight: Scores, tracks and reports enterprise risks to leadership.
- Third-party risk management: Centralizes assessments of vendor and supplier security.
- OpsAudit: Delivers audit management from planning to issue tracking.
Pricing
Optro quotes per deal. According to Vendr, the median contract is about $45,947 per year (third-party estimate, pre-rebrand data).
Hyperproof
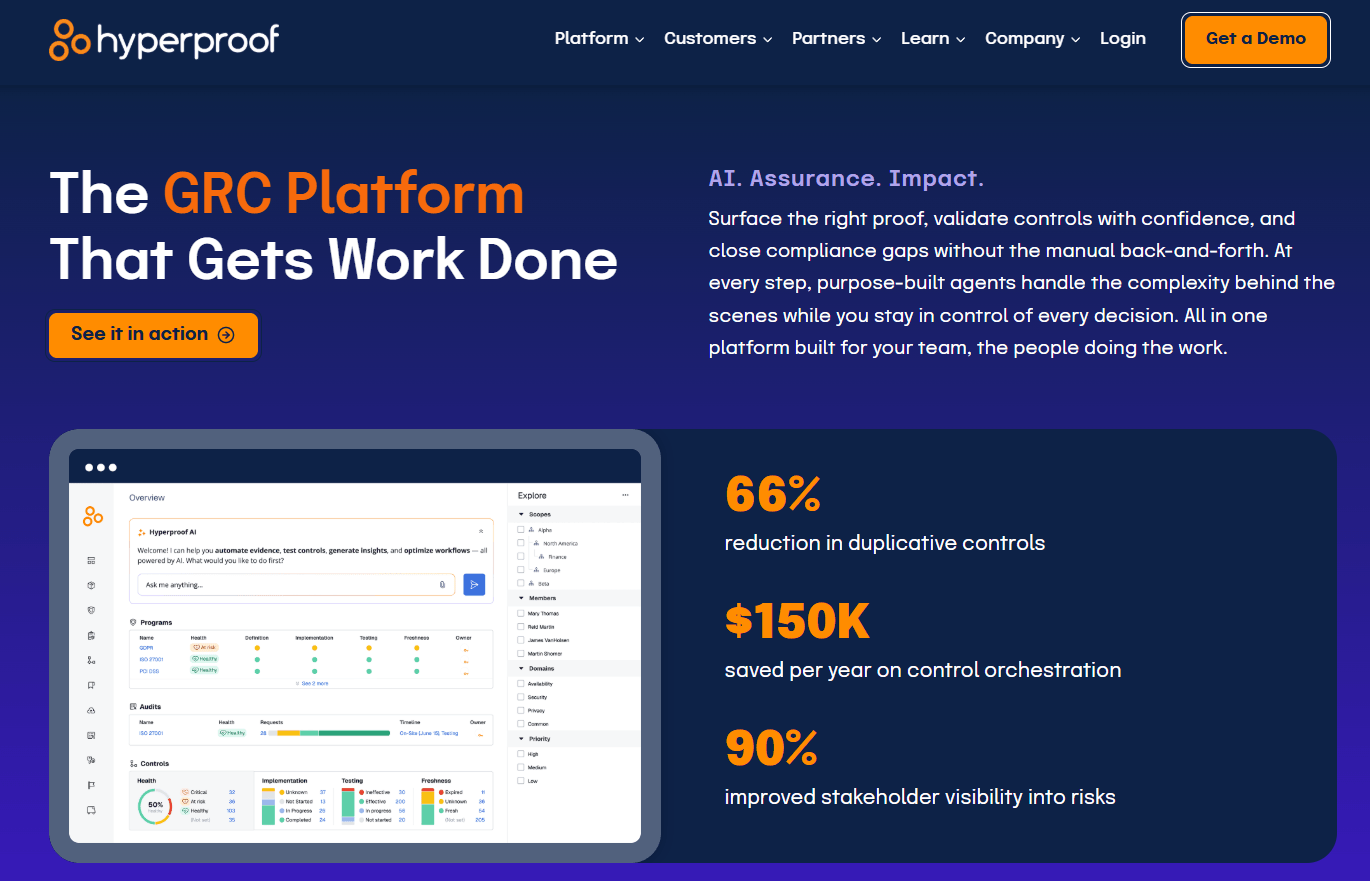
Source: Hyperproof website screenshot. Reviewed October 13, 2026.
Hyperproof, a compliance operations platform, treats audits as ongoing team work, not a yearly project. You prove a control once and reuse that proof across audits, so growing compliance programs stay manageable.
Best for
Mid-market and enterprise teams running multiple compliance frameworks from one shared control set.
Key features
- Automated control mapping: Links each control to internal and external standards across 160+ prebuilt frameworks.
- 200+ integrations: Connects tools like Jira and ServiceNow for automated workflows.
- Risk register: Scores and treats risks linked to their controls and evidence.
- Vendor risk management: Centralizes supplier questionnaires and findings with AI-assisted assessments.
- Dashboards and reporting: Lets leaders track compliance status by framework or team.
Pricing
Hyperproof also quotes per deal. According to Vendr, its median contract is about $41,400 per year, ranging from $22,215 to $70,000 (third-party estimate).
Secureframe
Source: Secureframe website screenshot. Reviewed October 13, 2026.
Secureframe, a security compliance platform, pairs its software with more than 30 in-house compliance experts and former auditors. That is rare among self-serve tools. For ISO® 27001 and TISAX®, see Valiido vs Secureframe.
Learn more about Secureframe competitors.
Best for
SaaS startups chasing a first SOC 2 or ISO® 27001 report before a sales deadline.
Key features
- Automated tests: Checks cloud settings against security controls and flags failures.
- Comply AI: Suggests fixes and drafts risk treatments for failing tests.
- Questionnaire automation: Answers security questionnaires with AI, using your existing evidence.
- Trust Center: Shares certifications and security documents with prospects.
- Personnel management: Tracks onboarding, offboarding and each employee's compliance tasks.
Pricing
Secureframe quotes all three plans. Third-party estimates start near $7,500 per year for one framework, with a Vendr-reported median near $20,000.
Vanta
Source: Vanta website screenshot. Reviewed October 13, 2026.
Vanta, a trust management platform, is known for fast, automated compliance management for SaaS. It pulls data from 400+ tools, the largest integration library on this list, and serves over 16,000 customers.
Best for
SaaS companies that need SOC 2 or ISO® 27001 fast and will add frameworks later. If ISO® 27001 or TISAX® is your main target, compare Valiido vs Vanta.
Key features
- Continuous compliance monitoring: Tests controls around the clock and alerts owners to failures.
- Vanta AI Agent: Drafts policies, completes questionnaires and flags issues for review.
- Trust Center: Shares real-time compliance status with customers and prospects.
- Multi-framework mapping: Reuses controls and evidence across 35+ frameworks, including ISO® 42001.
- Public API: Lets engineers push custom evidence and tests.
Pricing
Vanta quotes all four tiers. According to Costbench, Essentials starts around $10,000 per year for one framework, with a median near $20,000 (third-party estimate).
How to Choose the Right Compliance Automation Software
Picking compliance software comes down to three things: your framework, team size and how much of your stack needs live checks.
ISMS platforms fit ISO® 27001 and TISAX®. Broad automation suites serve SaaS, and enterprise GRC handles large risk programs.
Match the software to your team size and maturity
Small teams need guided tools and templates to maintain compliance between audits without designing compliance workflows from scratch. Enterprises need integrated risk management, role-based access and board reporting.
A 30-person agency and a 3,000-person bank should not buy the same tool.
Check integration depth and workflow fit
Integration depth decides how much evidence arrives on its own. Look for cloud and identity connectors, real-time alerts and workflow automation that syncs tasks to Jira.
Automated compliance workflows only pay off when they reach systems your team already uses. If your engineers live in Jira, a tool that cannot create tickets there will not stick.
Continuous compliance vs point-in-time readiness
Continuous monitoring checks controls every day, while point-in-time readiness proves compliance on one audit date. Daily checks suit large, fast-changing cloud environments.
According to IBM's Cost of a Data Breach Report 2026, the global average breach cost reached a record $4.99 million.
A lighter tool with scheduled checks covers a one-off certification or stable office IT. Either way, continuous oversight beats rebuilding evidence before each audit and makes ongoing compliance cheaper.
Six vendor questions to ask before you buy
- How does the tool ingest evidence, and how often?
- Which integrations and APIs come included?
- How does it map frameworks and controls automatically?
- Does it keep audit trails and version history?
- How long is onboarding, and what support do you get?
- What is the pricing model, and which costs sit outside it?
Which option fits your use case
- Valiido: A guided, fixed-price path to ISO® 27001 and TISAX®.
- Vanta: Rapid SOC 2 and ISO® 27001 onboarding.
- Optro: Compliance linked to enterprise audit and risk.
- Hyperproof: Detailed control mapping and reporting.
- Secureframe: Fast audit preparation with expert support.
Want more options? See our best ISMS software list.
Why Valiido Is the Best Compliance Automation Software
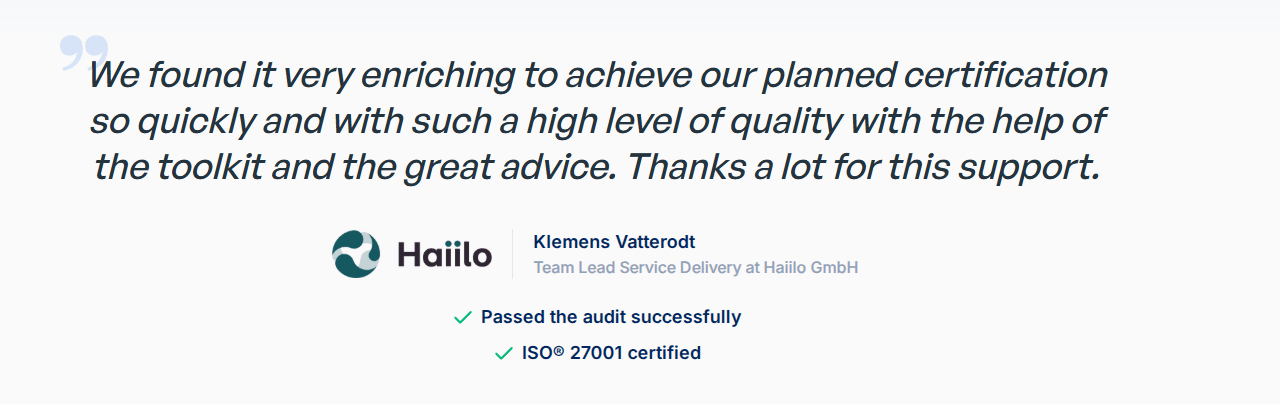
You want to pass your audit the first time, without paying a consultant to get you there. Our customers pass 98.7% of their audits on the first attempt. They rate Valiido, the ISMS software for ISO® 27001 and TISAX®, 4.9 out of 5 across 29 reviews.
You do not need an in-house expert or a consultant on retainer. A guided path tells your team what to do next. Weekly automated checks catch gaps early, and public flat pricing rules out surprise renewals.
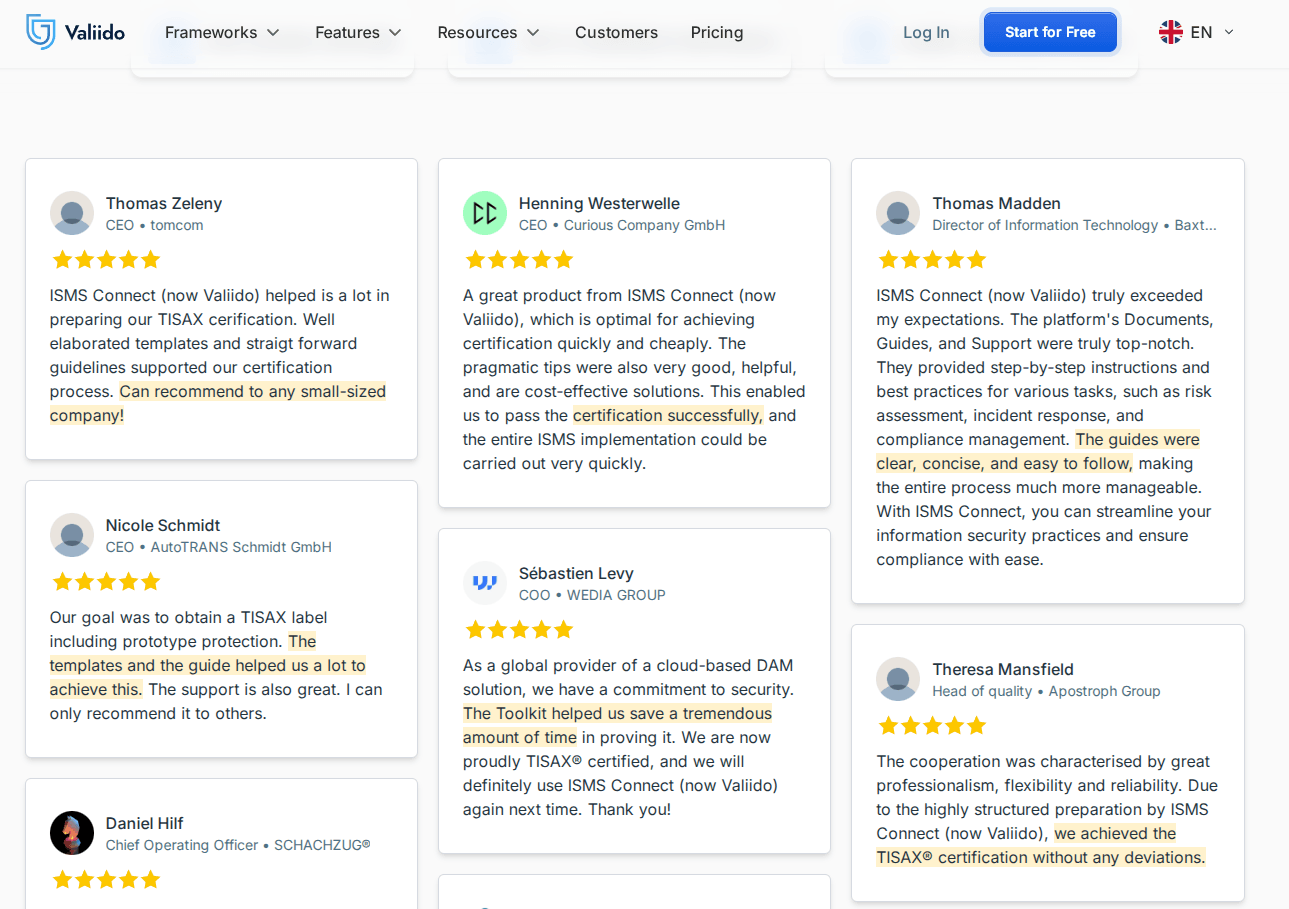
Together, they keep small companies' compliance efforts on budget and on schedule. TE Force GmbH, for example, earned the TISAX® AL3 label with a score of 2.9 out of 3.
Is it right for everyone? No. Valiido covers ISO® 27001 and TISAX® only, so if you need SOC 2 or 30+ frameworks, weigh that first.
What makes Valiido different
- Get a clear next step: The chapter-by-chapter guide walks non-specialists through the entire compliance process.
- Catch gaps before your auditor does: AuditMagic, our automated ISMS audit tool, checks records as you edit for continuous audit readiness.
- Skip the add-on upsell: Every plan includes every module, from risks and vendors to assets and audits.
- Budget with confidence: Plans cost €149 or €299 per month, published openly on the website.
- Keep the work you have done: An expert migrates your existing ISMS for free and reviews it before the audit.
Valiido vs other compliance automation tools
| Valiido | Optro | Hyperproof | Secureframe | Vanta | |
|---|---|---|---|---|---|
| Setup approach | Guided self-service | Enterprise rollout | Guided onboarding | Expert-led onboarding | Self-serve |
| Pricing transparency | Public flat price | Quote-only | Quote-only | Quote-only | Quote-only |
| Modules included | All, every plan | Separate products | Plan-based | Tiered | Tiered |
| Consultant needed | No | Optional | Optional | Optional; experts included | Optional |
| Framework focus | ISO® 27001, TISAX® | SOX, enterprise GRC | 160+ frameworks | SOC 2, CMMC and more | 35+ frameworks |
| Audit pass rate | 98.7% first attempt | Not published | Not published | Not published | Not published |
Want to see how quickly you could be audit-ready? Start for free and open your first chapter today, no credit card needed.
A Six-Step Checklist for Audit Readiness
A focused SMB team can map, build, test and document its ISMS in six steps. With the right platform, you can then follow an ISO® 27001 certification in 12 weeks plan.
Your first 30 days with a compliance automation platform
- Map your frameworks: List your regulatory requirements and single-source shared controls.
- Validate integrations: Confirm cloud, identity and people-data connectors with IT.
- Assign owners: Give every control and recurring task one named owner.
- Adopt templates and assess risks: Start from templates, rate your threats and plan how to mitigate risks.
- Pilot monitoring: Switch on automated checks for one area and fix what they flag.
- Document ROI: Record hours saved to show operational efficiency gains.
Final Words About Best Compliance Automation Software
Automation removes the manual evidence work that drains small teams. Just make sure the platform's scope fits this audit and the next few.
Optro fits enterprise audit and risk, and Hyperproof handles complex mapping. Secureframe speeds up SOC 2 work, while Vanta suits rapid SaaS onboarding.
Valiido is the strongest pick if you want a guided, fixed-price route to ISO® 27001 and TISAX®. Software helps you maintain compliance standards, but people still judge risks and close gaps.
Start for free and see your first gaps this week.
Frequently Asked Questions
What are the best compliance automation tools?
Five leading options are Valiido for guided ISO® 27001 and TISAX® prep, Vanta for fast SaaS onboarding and Secureframe for first SOC 2 audits. Hyperproof leads on control mapping, and Optro covers enterprise GRC. The comparison table lists G2 scores and pricing.
What are the top 5 GRC tools?
Five widely used GRC tools are Optro, Hyperproof, ServiceNow GRC, Archer and MetricStream. GRC suites manage enterprise-wide risk, audit and regulatory adherence, while automation-first tools focus on evidence. Optro and Hyperproof bridge both, adding automated testing to classic risk and compliance work.
What is the best software for tracking compliance?
The best software for tracking compliance matches what you track most. Vanta and Secureframe handle live cloud control tests, while Optro covers audit plans. Valiido and Hyperproof are strong on policy management, and each lets you monitor compliance status from one dashboard.
What is the best software for compliance training?
Compliance training usually runs on a dedicated security awareness platform with courses, phishing simulations and completion tracking. Vanta and Secureframe add basic awareness modules. Add data protection training too, since data protection regulations such as GDPR touch everyone's daily work.
How we evaluated & sources
This comparison was reviewed on October 13, 2026. It uses publicly available official product and pricing pages from Valiido, Optro, Hyperproof, Secureframe and Vanta, G2 ratings as of October 2026, and third-party pricing data from Vendr and Costbench where a vendor does not publish list prices. Every platform was assessed against the same five criteria: framework coverage, automation depth and integrations, scalability, ease of setup and pricing transparency. Details about Valiido also reflect direct product knowledge. Third-party price estimates are marked as such, and third-party screenshots are identified by source and review date.